NeoSystems ISG is under new ownership — backed by FIT Solutions. Rebuilt by people who know this business.
Read our story →

Managed IT · Hosting · Microsoft Cybersecurity · CMMC

Built for GovCon.
Proven in Audits.

Under new ownership since May 2026 — new mission, honestly run.

We don't adapt generic IT services to fit CMMC — we built our practice around it from day one. For government contractors who handle CUI and can't afford to fail an assessment.

CMMC 2.0 · NIST 800-171Readiness & C3PAO prep
GCC & GCC HighMicrosoft 365 enclaves
FedRAMP-aligned cloudAzure Government hosting
Concrete federal-style building photographed from below at dusk, with illuminated windows
CMMC Level 2 Certified MSPA 20-year GovCon practice, rebuilt under new ownership.
20+

Years serving government contractors across the Defense Industrial Base

100s

Of DIB contractors supported nationwide with CMMC compliance services

2003

Year founded — compliance has been core to our practice from the start

Level 2

CMMC Certified MSP — purpose-built controls, evidence, and audit preparation

Why contractors choose NeoSystems ISG

Compliance without building it all yourself

Most small and mid-sized contractors don't have a large in-house compliance or cybersecurity team — and they don't need one. They need a partner whose systems, evidence, and people are already built for the audit.

01

Faster path to compliance

Purpose-built solutions and pre-documented controls get you to audit-ready faster than building from scratch internally.

02

Reduced audit risk

Audited, proven solutions with tangible evidence packages — you walk into your C3PAO assessment prepared.

03

Compliance that stays current

Continuous monitoring and a compliance dashboard keep your posture strong as requirements evolve.

04

Accessible for small & mid-sized contractors

Scalable, affordable solutions built for companies without large in-house compliance or cybersecurity teams.

The rebuild, in plain numbers

We tell you what happened — including the hard parts.

41% of clients stayed

41% of clients stayed with us through the collapse — and we're earning the rest back.

A dozen rehired

A dozen of the original team came back to rebuild — people who knew the clients and chose to return.

Privately owned

Privately owned and run by an experienced team in managed IT and cybersecurity for the defense industrial base — no outside investors, just clients to answer to.

A 20-year GovCon practice, rebuilt under new ownership. Read the full story →

Our Story

“We intend for this to be one of the great comebacks in our industry.”
What happened — and why we bought it anyway →
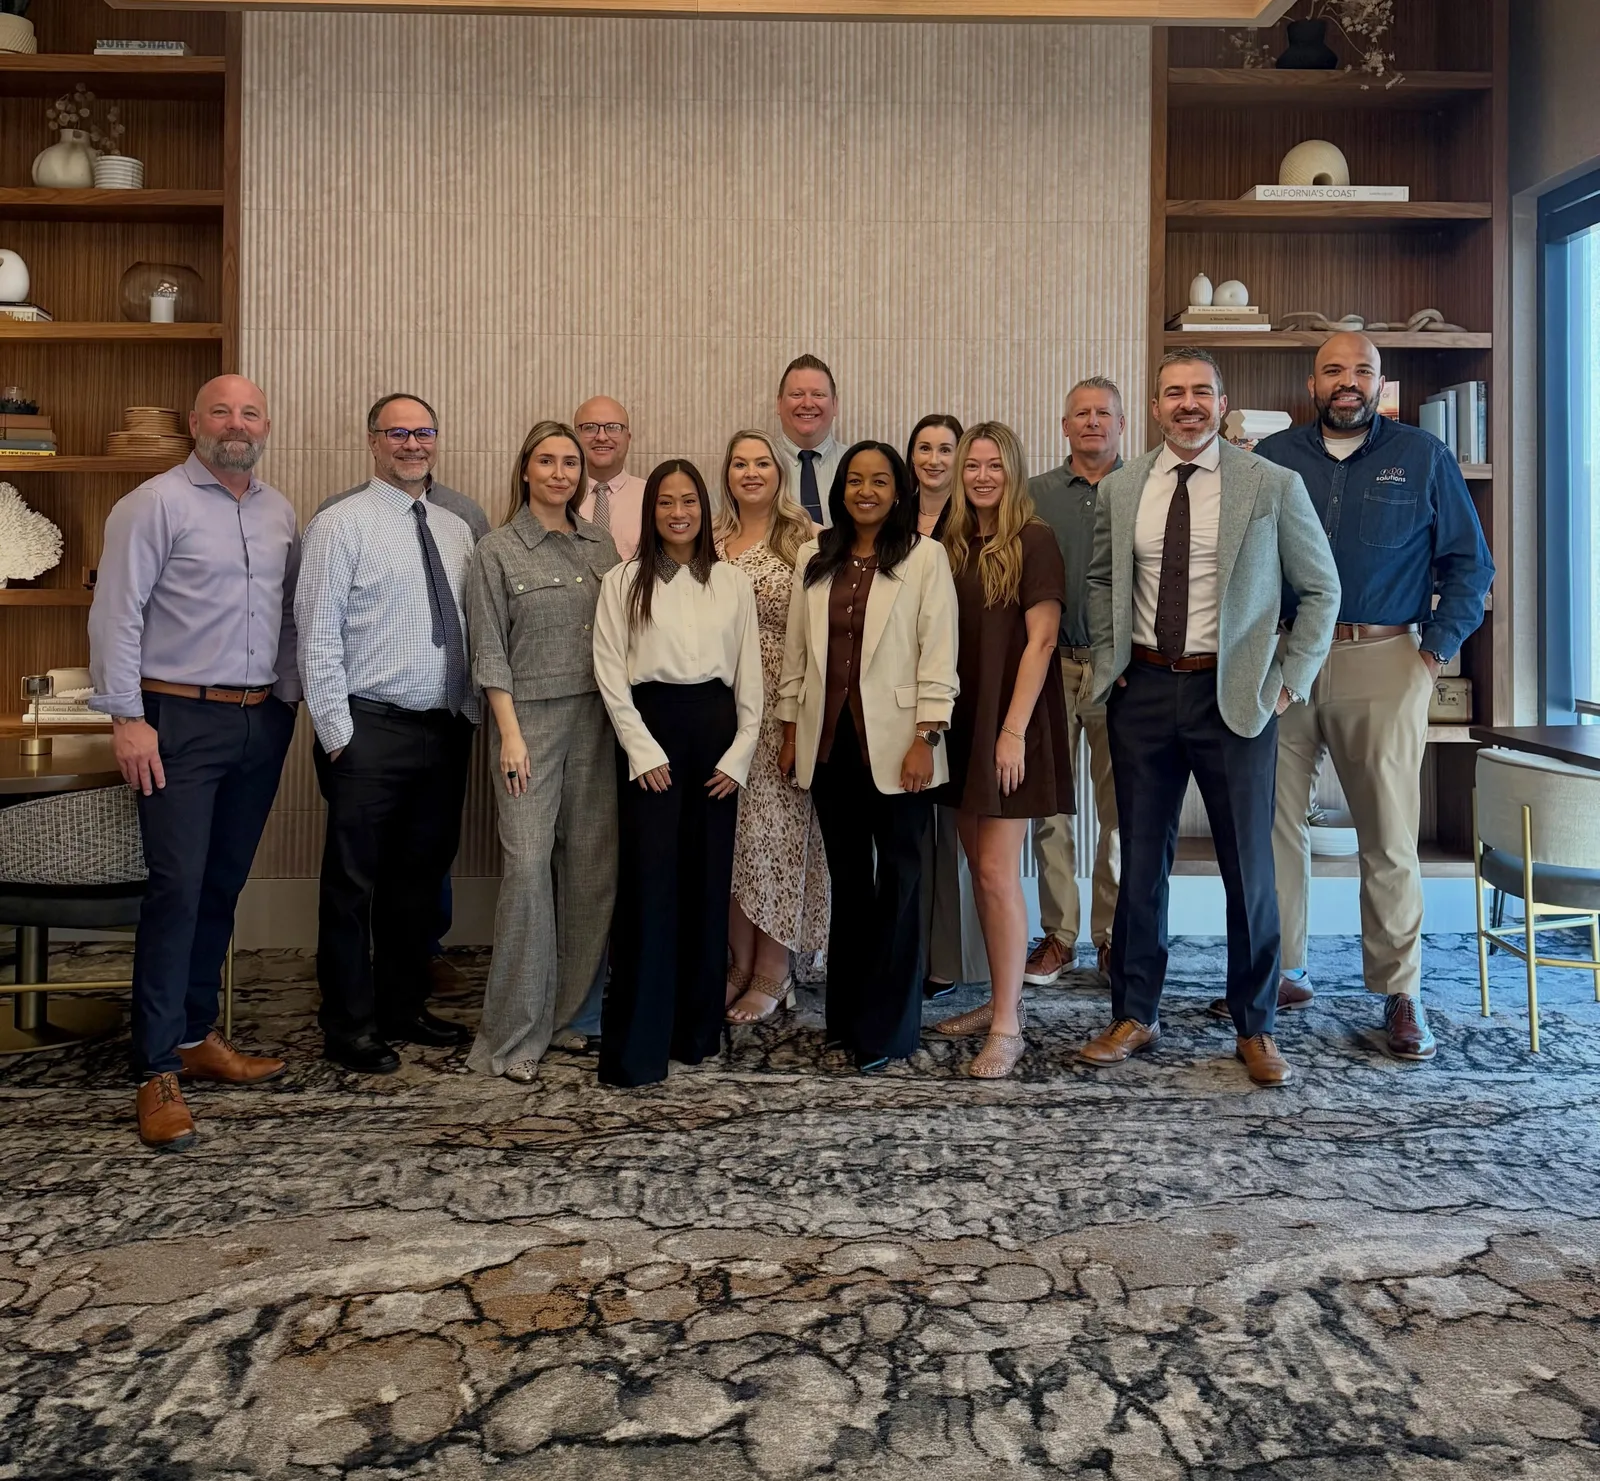
The NeoSystems ISG team standing together in the office

What our clients say — then and now

A renewed sense of partnership

“Just wanted to check in and say thanks to your team for doing a great job in supporting AMA’s System! NeoSystems ISG has provided a seamless transition to managing AMA’s hosting and services.”

Dennis Bulgatz Analytical Mechanics Associates

“NeoSystems gave us a renewed sense of partnership. The attitude is ‘we're going to figure out a way to get it done’, and I can't tell you how priceless that is.”

Elissa Passiment Executive VP, American Society for Clinical Laboratory Science

Contact Us Today

Tell us where you are on CMMC, GCC High, or hosting — we'll tell you honestly what it takes to get audit-ready.

Services for government contractors

CMMC, GCC High, FedRAMP-aligned cloud — done for you, not dumped on you.

If you handle Federal Contract Information or Controlled Unclassified Information, your IT is your compliance. These four practices keep it secure, documented, and assessment-ready.

01 · CMMC Compliance

Get to Level 2 — and stay there

For primes and subs in the Defense Industrial Base facing CMMC 2.0 flow-downs in contracts.

CMMC 2.0 readiness built on NIST SP 800-171: we implement the controls, document the evidence, and prepare you for your C3PAO assessment — then keep you current after you pass.

If your applications store, process, or transmit CUI, DFARS 252.204-7012 applies, and NIST SP 800-171 is the standard you have to meet. CMMC Level 2 is how you prove it.

And when something happens, we support your DFARS 252.204-7012 obligation to report cyber incidents within 72 hours, with the documentation the DoD requires.

  • CMMC 2.0 readiness & gap assessment
  • NIST SP 800-171 implementation (110 controls)
  • SPRS scoring & submission support
  • POA&M creation & management
  • Evidence packages an assessor can follow
  • C3PAO assessment preparation & mock review
  • System Security Plan (SSP) development
  • Continuous monitoring & compliance dashboard
Why it’s faster with us: Purpose-built solutions and pre-documented controls get you to audit-ready faster than building from scratch internally — with tangible evidence, not promises.

02 · Microsoft 365

GCC & GCC High, migrated and managed

For contractors whose CUI or ITAR data can’t live in commercial Microsoft 365.

We move you into the right Microsoft government cloud — and run it day to day, configured to the controls your contracts require.

  • Seamless GCC migration planning & execution
  • GCC High enclaves for CUI / ITAR workloads
  • Licensing guidance — buy only what you need
  • Security & compliance configuration to 800-171
  • Identity, MFA & conditional access hardening
  • Ongoing management of the Microsoft environment
GCC or GCC High? If you handle ITAR data or CUI that requires GCC High’s stricter boundary, we’ll scope it honestly. If standard GCC meets your contracts, we won’t oversell you High. Ask us which you need →

03 · Cloud & Hosting

FedRAMP-aligned cloud & managed hosting

Hosting restored — and run — for the defense industrial base.

Managed hosting for contractors, operating your workloads in FedRAMP-authorized cloud environments — including Azure Government — so the platform beneath your CUI already meets federal authorization requirements.

  • Workloads in FedRAMP-authorized environments (Azure Government)
  • Managed hosting for GovCon applications & data
  • Backup, recovery & continuity for CUI systems
  • Hosting operations, patching & monitoring included
Stated precisely: NeoSystems ISG helps contractors operate in FedRAMP-authorized cloud environments. We don’t claim FedRAMP authorization for ourselves — the authorization belongs to the cloud platforms we build on, and that distinction matters in an audit.

04 · Cybersecurity

Managed cybersecurity, Microsoft-first

Security coverage without hiring a full in-house SOC.

Our Microsoft cybersecurity practice protects the same environment your compliance depends on — one team, one throat to choke, no gaps between “IT” and “security.”

  • Microsoft cybersecurity stack management
  • Continuous monitoring / SOC coverage
  • Endpoint & identity protection
  • Incident response & remediation support
  • Vulnerability & patch management
  • Security sized for small & mid-sized contractors

How an engagement runs

From gap to audit-ready — tap a step

1 · Assess — know your real score

We assess you against all 110 NIST SP 800-171 controls, calculate your SPRS score honestly, and show you exactly what stands between you and Level 2 — in plain language, with a costed plan.

Not sure where you stand?

Start with an assessment. We’ll tell you your gap — even if the answer is “you need less than you feared.”

Our Story · Told honestly

What happened to NeoSystems ISG — and why we bought it anyway

NeoSystems ISG collapsed on May 14, 2026. NSISG Holding LLC bought the ISG business when nobody else would touch it. This is what happened — the collapse, the two weeks customers sat in the dark, and the rebuild since.

May 14, 2026NSISG Holding LLC bought ALL of the ISG business
41% stayedOf clients stayed through the transition
A dozen returnedOriginal staff who came back to rebuild

The Collapse

Before our acquisition, NeoSystems experienced a business failure and serious service disruptions. Customers lost access to systems they depended on. Communication broke down. Experienced employees were displaced, and trust built over years was damaged.

For government contractors with operational deadlines and compliance obligations, the consequences were severe. We understand why customers were frustrated and why many chose to leave.

We did not own the business when those events occurred. Once we acquired ISG, we took responsibility for the work ahead.

New ownership. Rebuilding the NeoSystems ISG legacy.

NeoSystems ISG built its reputation on experienced people helping government contractors manage complex technology, security, and compliance requirements. Almost all of that was lost in a single day. When the business failed, the expertise and relationships that made it valuable were still worth preserving.

How our team responded

On May 14, 2026, NSISG Holding LLC acquired the ISG business. Within hours, we were on the phone with customers who had been without support for two weeks. Some were angry, some were grateful, and all of them needed answers. We started there.

Our first priority was helping every customer move forward.

For those who chose to leave, we helped them transition. That meant giving up revenue, but we believed customers deserved a workable path forward after what they had experienced.

For those who stayed, our team focused on restoring service, resolving outstanding issues, supporting their CMMC compliance work, and reestablishing communication.

The Rebuild

We rehired the team members our clients valued most, and in the process restored many good jobs. They brought technical experience, customer relationships, and an understanding of what NeoSystems ISG had once represented. Together, we began rebuilding the business around the strengths that had earned customers’ trust in the first place.

Who we are

Our ownership is led by Ephraim Alexander Ebstein, an engineer by trade who built his businesses organically, without private equity or venture capital backing. That growth came through earning people’s trust, delivering on commitments, and building teams that customers could rely on.

That background reflects the founding principles NeoSystems was built on before private equity ownership: technical expertise, personal relationships, and dependable service as the foundation of a lasting business. Because we answer to customers, not investors, we could move fast and acquire NeoSystems ISG in its darkest moment, taking on a rebuild few others were willing to attempt.

But rebuilding NeoSystems ISG is much bigger than one person. It is the work of engineers, cybersecurity and compliance professionals, service teams, and leaders who bring their experience and judgment to our customers every day. Our team includes returning NeoSystems colleagues whose knowledge of these environments and relationships with customers are central to the rebuild.

We bring together experienced ownership and the people who do the work. Both matter. Leadership is responsible for giving our teams the direction, resources, and support to deliver, and our customers should know who is accountable.

What we are building

Today, NeoSystems ISG is owned by NSISG Holding LLC. We provide managed hosting, Microsoft 365 GCC, cybersecurity, and CMMC compliance services for government contractors.

Our approach is simple: listen carefully, make commitments we can deliver on, give our people the support to do their jobs well, and address problems directly.

We believe technical quality and responsible business management belong together. A dependable company must invest in its people, maintain its systems, and operate sustainably so customers can count on it over time.

We know new ownership does not automatically restore confidence. That confidence must be earned through the experience customers have with our entire team.

Moving forward

For customers who gave us a shot, thank you for giving us the opportunity to earn your confidence. For those who left, we understand why, and the door remains open.

For those meeting us for the first time, we welcome questions about our ownership, our people, and how we support your business.

We are proud of the expertise behind the NeoSystems ISG name today. We intend for this to be one of the great comebacks in our industry. Together, we are working to earn its reputation every day.

Blog · Insights for the Defense Industrial Base

Compliance, in plain English.

Practical guidance for government contractors on CMMC, Microsoft GCC & GCC High, FedRAMP-aligned cloud, and the audits that decide whether you keep your contracts. New posts published regularly.

Compliance operations desk with a November calendar page, shield emblem and contract documents in front of a federal office building at dusk, gold network lines, in navy and gold
GovCon IT & Cybersecurity

Federal Contractor Compliance After November 10: The Deadline Passed, the Duties Did Not

November 10 passed without Phase 2. What did not pause: DFARS 7012 safeguarding, honest SPRS self-assessments, the 72-hour reporting path, and same-day KEV triage — and what primes are asking for as proof.

Read article →
Secure cloud operations wall in front of a federal office building at dusk, gold network lines connecting a contractor office to authorized cloud data centers, a shield emblem and contract document, in navy and gold
FedRAMP & Federal Cloud

DFARS 7021 Compliance: What the Clause Requires From Your Cloud Providers Before Award

DFARS 7021 ties your CMMC status to the cloud providers you use. How to verify FedRAMP authorization or equivalency, flow the clause down, and record provider status before award.

Read article →
Senior executive signing a formal compliance document at a desk in front of a federal office building at dusk, gold shield emblem, in navy and gold
CMMC Compliance

CMMC Level 2 Certification and the Annual Affirmation: What Your Senior Official Is Actually Signing

After certification, a senior official must affirm continuing CMMC compliance in SPRS every year. The affirmation packet, the three review questions, and the calendar rhythm that make that signature defensible.

Read article →
Secure operations center at dusk in front of a federal office building, a wall display with gold three-day patch timeline markers and a shield emblem, in navy and gold
Cybersecurity

GovCon IT Services on a Three-Day Clock: What November's KEV Surge Requires From Contractors

CISA added ten exploited flaws in two days, with a three-day federal deadline on the first batch. The triage-first, patch-second playbook — and the inventory and evidence record contractors need before the next batch lands.

Read article →
Secure operations wall with a gold world map and export routes stopping at a glowing boundary, a controlled technical blueprint and a shield emblem beside an aerospace facility at dusk, in navy and gold
Cloud & Hosting

GCC High: When ITAR and Export-Controlled Work Make It the Only Tenant That Fits

ITAR technical data turns your tenant into an export-control boundary. When the data and the clauses require GCC High, what it changes about people, support, and data location — and what stays yours.

Read article →
Assessor evidence review table in a secure office at dusk with organized binders, a laptop checklist dashboard and a shield emblem, gold lines tracing documents to control checkmarks in front of a federal office building, in navy and gold
CMMC

Defense Contractor Cybersecurity: Building the Evidence File That Passes a CMMC Level 2 Assessment

A CMMC Level 2 assessment is scored objective by objective on evidence an outsider can follow. The file to build — scope, records across time, technical captures, and provider proof — before the C3PAO arrives.

Read article →
Secure supply chain operations wall at dusk with interconnected supplier nodes linked by gold lines converging on a shield emblem in front of a federal office building, in navy and gold
Cybersecurity

Supply Chain Risk Management: GSA's New Monitoring Clause Puts Your Suppliers in Your Compliance File

GSA can now remove an offeror for supplier risk and act during performance under GSAR 552.540-70 and 552.540-71. The supplier inventory, flow-down, and mitigation file to build before the clause lands in your contract.

Read article →
Secure cloud tenant dashboard over a federal office building at dusk, gold boundary lines separating inherited platform controls from tenant configuration controls, shield emblem, in navy and gold
Cloud & Hosting

Microsoft 365 GCC: What You Inherit, What You Must Configure, and What You Still Own

Inheritance is real, but partial. The controls Microsoft covers, the tenant settings that decide whether CUI stays inside your boundary, and the evidence an assessor will ask for — mapped.

Read article →
Compliance operations wall at dusk with a gold calendar grid and checklist board, shield emblem, and federal office building in navy and gold
CMMC

CMMC Compliance Is a Calendar, Not a Project: The Maintenance Rhythm That Keeps Your Status Valid

Certification is the start, not the finish. The annual affirmation, the 180-day POA&M clock, SSP reviews, and the change events that quietly break scope — on one maintenance calendar.

Read article →
Security operations center at dusk monitoring an edge firewall and VPN gateway in navy and gold with a shield emblem and clock motif
Cybersecurity

DFARS Incident Reporting: Why This Week's KEV Deadlines Start Your 72-Hour Clock Before a Breach Is Confirmed

Two exploited flaws, two three-day federal clocks in one week. Why discovery, forensic triage, and evidence preservation must run in parallel with patching, before compromise is confirmed.

Read article →
Secure cloud data center at dusk in navy and gold with a gold boundary line around a hosted server enclave
Cloud & Hosting

CUI Cloud Hosting: When a Productivity Tenant Is Not the Right Home for CUI

Large files, applications, and ITAR workloads fit poorly in a productivity tenant. How to place them in managed hosting on an authorized foundation, and draw GCC, GCC High, and hosting as one boundary.

Read article →
Prime contractor headquarters at dusk connected by gold network lines to subcontractor facilities with a shield emblem
CMMC

CMMC 2.0 Requirements: Flow-Down to Subcontractors — What Primes Must Send Down and Subs Must Prove

Flow-down is not forwarding a clause. How primes define the level, scope, and evidence for subs handling CUI — and what subs must be ready to prove before they are asked.

Read article →
Federal building at dusk connected by gold network lines to a security operations center with a shield emblem
Cybersecurity

Government Contractor Cybersecurity After the CMMC Phase 2 Pause: What Did Not Pause

Phase 2 is suspended, but DFARS 7012, SPRS, and the 72-hour reporting clock never stopped. October’s CISA deadlines and supply-chain orders underline it: what still applies, and what to do before year end.

Read article →
Federal-style building and secure cloud data center at dusk with a gold boundary line
Cloud & Hosting

DFARS 7012 Compliance in the Cloud: What Your Provider Covers — and What Stays Yours

Moving CUI to a FedRAMP-authorized cloud changes who implements some controls — not who is accountable. Where the shared-responsibility line actually falls, and what stays yours to prove.

Read article →
Abstract steel panels on a blueprint grid with a gold enclave boundary
CMMC

NIST 800-171 Compliance: How to Scope CUI and Build an Enclave That Holds Up

Compliance fails at scoping, not at testing. Walk your real CUI flow, draw a smaller boundary you can defend, and build an enclave that holds up when the assessor arrives.

Read article →
Government building under a digital cloud
GCC & GCC High

GCC vs. GCC High: Which Microsoft Cloud Does Your Contract Actually Require?

ITAR, CUI, and flow-down language point to different answers. How to read your contract before you buy licenses you don’t need — or skip the enclave you do.

Read article →
Navy radar grid with a single gold point
CMMC

SPRS Scores, Explained: What Your Number Says About You to a Prime

Your SPRS score is visible, comparable, and increasingly decisive in subcontract awards. What goes into it — and how to raise it honestly.

Read article →
Abstract steel panels on a blueprint grid
CMMC

POA&Ms Without Panic: Closing Gaps in the Right Order

Not every gap carries the same risk or the same fix time. A practical order of operations for working a POA&M down before your assessment window opens.

Read article →
Federal-style building at dusk
Cloud & Hosting

Operating in FedRAMP-Authorized Cloud: What It Means — and What It Doesn’t

“FedRAMP-aligned” gets used loosely. What authorization actually belongs to the cloud platform, what remains your responsibility, and what assessors check.

Read article →
Abstract steel panels on a blueprint grid
Cybersecurity

Continuous Monitoring Is the Control: Staying Compliant After You Pass

Passing an assessment is a snapshot. Contracts, primes, and CMMC itself expect an ongoing posture — here is the monitoring rhythm that keeps you there.

Read article →
Federal-style building at dusk
GCC & GCC High

Migrating to GCC High Without Breaking the Business

Mailbox moves are the easy part. Identities, files, Teams, and third-party apps are where migrations stall — a phased plan that keeps people working.

Read article →
How to use this index in WordPress: each card is a post (featured image, category, title, excerpt, date, read time), newest first. The featured post at the top is the latest CMMC article and opens the sample article template.

Reading is good. Audit-ready is better.

Get a readiness assessment for your own environment — SSP, SPRS, and evidence included.

← Back to Blog

CMMC · Assessment Preparation

CMMC Assessment Preparation: What to Have Ready Before the C3PAO Arrives

Your assessment is not the time to discover missing evidence. This is the readiness sequence we run with government contractors — so the assessor finds a system that is documented, operating, and provable.

Server racks behind a locked security cage in a data center

Most contractors don’t fail a CMMC Level 2 assessment because their technology is wrong. They fail — or stall, or burn months they don’t have — because the evidence isn’t ready. A control can be implemented and still be unprovable on the day. Assessment preparation is the discipline of closing that gap before a C3PAO ever logs in.

This article is the template we want every post on this site to follow: a clear promise up front, short sections an executive can scan, specifics a compliance lead can act on, and one honest call to action at the end. If you are reading it as a contractor rather than a designer, start with the checklist in the middle — it is the order we actually work in.

1. Your SSP is the assessment

Your System Security Plan is not paperwork that accompanies the assessment; in large part, it is the assessment. Assessors test what your SSP says you do. If the SSP describes an environment that no longer exists — old tools, departed staff, a network diagram from two reorganizations ago — every interview that follows starts with a credibility problem.

  • Scope first: name exactly which systems, people, and locations handle CUI. Everything else follows from that boundary.
  • Control by control: for each of the 110 NIST SP 800-171 controls, state how it is met, by what, and where the evidence lives.
  • Keep it alive: an SSP updated at last year’s assessment and untouched since is a finding waiting to happen.

2. Know your SPRS score before a prime asks

Your SPRS score is not an internal metric. Primes look at it, compare it, and — increasingly — select on it. Submitting an inflated score is worse than submitting a low one: it converts a gap you could have explained into an integrity question you can’t.

Submit the honest score, with a POA&M that shows the path. A low score with a credible plan reads as a contractor in motion. A perfect score you can’t evidence reads as a risk.

Score yourself the way an assessor would: a control is only “met” when it is implemented and you can show it. Partial credit is not how this works — and it is exactly why pre-documented controls and evidence packages matter.

The pre-assessment checklist

  • Current SSP with a defensible CUI scope and boundary diagram
  • Honest SPRS score submitted, with scoring worksheet retained
  • POA&M for every unmet control — owner, milestone, and date on each item
  • Evidence package indexed by control: screenshots, configs, logs, tickets, training records
  • Policies staff can actually describe in an interview — not just PDFs they signed
  • Incident response plan tested at least once, with the test documented

3. Work the POA&M in risk order, not list order

A POA&M worked top-to-bottom wastes your scarcest resource: calendar time before the assessment window. Work it by risk and dependency instead. Identity controls — MFA, privileged access, account management — unlock or block a surprising share of everything downstream. Logging and monitoring take time to produce the history assessors want to see, so they should start early even when they feel less urgent.

This is also where an enclave decision pays off. Moving CUI into a GCC High enclave or a FedRAMP-authorized cloud environment shrinks the scope you must bring to full compliance, which shrinks the POA&M with it. Scope reduction is the most underused readiness move we see.

4. Rehearse the interviews

Assessors interview people, not just systems. The engineer who runs backups, the office manager who onboards staff, the executive who owns the incident plan — each will be asked to describe, in their own words, processes your SSP claims exist. Thirty minutes of rehearsal per person, walking through “show me how you’d…” scenarios, prevents the most avoidable findings we encounter: the control that exists but nobody could explain.

What “ready” actually looks like

Ready does not mean perfect. It means: the scope is defensible, the score is honest, every gap has an owner and a date, the evidence is indexed before anyone asks for it, and your people can describe what they do. Contractors who arrive in that state don’t fear the assessment — they use it, because a passed Level 2 assessment is a competitive asset every time a prime builds a team.

And readiness is not a finish line. Continuous monitoring and a living compliance dashboard are what keep the posture you proved on assessment day true on every day after it.

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions. CMMC Level 2 Certified MSP.

Where does your readiness stand?

We’ll assess your SSP, SPRS score, and evidence the way a C3PAO will — and give you the honest gap list.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

← Back to Blog

CMMC · NIST 800-171

NIST 800-171 Compliance: How to Scope CUI and Build an Enclave That Holds Up

NIST 800-171 compliance starts with scoping CUI correctly. How government contractors build a defensible enclave, close POA&M gaps, and stay assessment-ready.

Abstract steel panels on a blueprint grid with a gold enclave boundary

NIST 800-171 compliance fails most often before a single control is tested. It fails at scoping. If you cannot say precisely where Controlled Unclassified Information lives, who touches it, and which systems protect it, the 110 practices in NIST SP 800-171 have nothing solid to attach to, and under CMMC 2.0 that uncertainty becomes findings, delays, and contracts at risk.

For government contractors, especially subcontractors handling CUI as part of a larger program, the practical path is not to drag the entire company into scope. Scope honestly, shrink the boundary where you can defend it, and implement NIST 800-171 compliance thoroughly inside that smaller boundary. An enclave does exactly that, when it is built on real data flow, not wishful thinking.

Start with where CUI actually flows, not where you hope it flows

Scoping starts with a data-flow walk, not an org chart. Follow one piece of CUI from arrival to departure: how it enters (email, a customer portal, a file transfer from the prime), where it is stored, who opens it, what applications process it, where it is printed or exported, and how it leaves.

Contractors are routinely surprised by what this walk finds: CUI in a general inbox, a drawing synced to a personal cloud account, an estimating spreadsheet on a shared drive the whole office can open. That was not a scoping decision, it was drift. Find the drift first, because your System Security Plan has to describe reality. An assessor who finds CUI outside your stated boundary will treat it as a boundary that cannot be trusted.

Document the flow in plain terms: sources, systems, people, and destinations. That document becomes the foundation for everything else, your asset inventory, your boundary diagram, and your SSP.

The enclave decision: smaller scope, stronger controls

An enclave is a defined segment of your environment, specific devices, accounts, applications, and network controls, where CUI is allowed to live, separated from the rest of the business. Email, estimating, engineering, and file work involving CUI happen inside the enclave. General business systems stay outside it.

For many contractors the enclave runs on Microsoft 365 GCC High or a FedRAMP-authorized cloud environment, because the platform carries a share of the control burden with it. That inheritance only counts if you can name which controls the platform meets and which remain yours. “The cloud provider handles it” is not an answer an assessor accepts.

“The cloud provider handles it” is not an answer an assessor accepts.

Done well, an enclave helps in three ways: it reduces cost, because you apply controls rigorously to a smaller set of assets; it makes evidence cleaner, because logs and access reviews all point to the same bounded environment; and it makes daily work clearer, if it involves CUI, it happens here, with these accounts, on these devices.

Done poorly, an enclave is just a diagram. The common failure modes are predictable:

Where enclaves fail

  • Porous boundaries. Staff use the same unmanaged laptop or the same password for general email and CUI work, so the separation exists on paper only.
  • Uncontrolled entry and exit. Files move in and out over personal email or removable media with no logging and no approval step.
  • Forgotten support systems. Backups, remote-access tools, endpoint management, and the cloud services that store or process CUI are themselves in scope, or security protection assets for the enclave. Leaving them out of the inventory is a scoping error assessors look for.

Map the 110 practices to the enclave, practice by practice

With the boundary drawn, map each of the 110 practices to how it is implemented inside the enclave. Be specific in the SSP: which system enforces it, which setting proves it, and who owns it.

A few families deserve extra attention in an enclave build:

  • Access control and identification. Unique accounts, least privilege, and multi-factor authentication for remote and privileged access. Shared accounts inside a CUI enclave are a finding waiting to happen.
  • Audit and accountability. Centralized logging that actually gets reviewed. Logs that no one reads do not satisfy the intent of the practice, and interview questions will surface that quickly.
  • Configuration and media protection. A documented baseline for enclave devices, limits on removable media, and a clear rule for printing and handling CUI, including what happens to paper after.
  • Incident response. A written plan, named roles, and at least one tested exercise. Under DFARS 252.204-7012, a cyber incident carries a 72-hour rapid-reporting obligation, and the enclave is where that clock will start. If enclave users cannot describe how they report a suspected incident, the plan is not operating.

Where a practice is not yet met, record it honestly in your Plan of Action and Milestones: the gap, the fix, the owner, and a dated milestone you can hit. A POA&M used as a parking lot does not help, and under CMMC 2.0, POA&M eligibility is limited, so do not assume every gap can ride one into an assessment. Keep your SPRS score aligned with the same honesty: score what is implemented today, update it as items close, and keep the SSP, the score, and reality in sync.

Keep people inside the boundary, too

Enclaves fail at the human edge more than the network edge. If the compliant path is hard, staff will route around it. Make it the easy path: the right applications, file sharing that works, and one rule staff can remember. CUI stays in the enclave, every time.

Train to that rule specifically: how to recognize CUI markings, handle a misdirected CUI email, report a suspected spill, and why personal accounts are out of bounds. Keep completion records, because training evidence and interviews are part of how implementation gets verified. Subcontractors need the same discipline: if a sub touches CUI, the requirements flow down. Confirm in writing what they handle and what evidence they can provide. Verbal assurance is not flow-down.

Operate the enclave like it will be assessed tomorrow

Contractors who stay ready treat the enclave as an operating environment, not a one-time project. Access reviews happen on schedule, patches and scans get documented, and enclave backups are tested, not just scheduled. Any change, a new app, cloud service, or remote-access path, triggers a scope check before it goes live.

Continuous monitoring helps in a practical way: around-the-clock monitoring generates the detection records and review logs that double as assessment evidence, while catching credential abuse between assessments. It is the difference between proving your posture once, on assessment day, and holding it every day after.

Before you schedule an assessment, sample CUI files and confirm each lives inside the enclave, interview two enclave users, and test one restore. If any fail, you have found your next POA&M item while it is still cheap to fix.

NIST 800-171 compliance does not require the biggest environment. It requires a truthful one, scoped to real CUI flow, separated where separation helps, documented practice by practice, and operated consistently after the project ends. Build that, and CMMC stops being a scramble.

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions. CMMC Level 2 Certified MSP.

Where does your CUI boundary stand?

NeoSystems ISG is a managed IT, hosting, and cybersecurity provider built for government contractors. We’ll review your SSP, SPRS score, and evidence the way a C3PAO will.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

NeoSystems ISG · UEI K5S3DCMK6SJ4 · CAGE 332H1

← Back to Blog

FedRAMP & Federal Cloud · DFARS 7012

DFARS 7012 Compliance in the Cloud: What Your Provider Covers — and What Stays Yours

DFARS 7012 compliance does not transfer to your cloud provider. How shared responsibility and inheritance really work in FedRAMP-authorized cloud, Microsoft 365 GCC and GCC High, and CUI cloud hosting — and what remains yours to prove.

Federal-style building and secure cloud data center at dusk with a gold boundary line

DFARS 7012 compliance does not transfer to your cloud provider. Moving Controlled Unclassified Information into a FedRAMP authorized cloud, Microsoft 365 GCC or GCC High, or a managed CUI cloud hosting environment changes who implements some controls. It does not change who is accountable when a prime, a contracting officer, or an assessor asks for proof. That accountability stays with the contractor whose name is on the contract.

That distinction is where many cloud migrations go wrong. A contractor buys the right platform, assumes the platform’s authorization covers the whole obligation, and discovers months later that identity, configuration, evidence, and incident reporting were theirs all along. Shared responsibility is real and valuable. It is also partial, and DFARS 7012 compliance depends on knowing exactly where the line falls.

What DFARS 252.204-7012 actually puts on you

The clause does two main things. First, it requires adequate security for covered defense information on your systems, which in practice means implementing the requirements in NIST SP 800-171 for systems that store, process, or transmit CUI. Second, it requires rapid reporting of cyber incidents to the Department of Defense, within 72 hours of discovery, along with preservation of images and relevant monitoring and packet data and cooperation with a DoD investigation.

Neither obligation names your cloud provider. Both name you. The clause also flows down to subcontractors whose work involves covered defense information, so a sub cannot treat a prime’s platform as a substitute for its own compliance, and a prime cannot assume a sub’s cloud choice settles the sub’s obligations.

Cloud changes the implementation, not the obligation. That is the starting point for every decision that follows.

Inheritance is real — but it is partial, and it has to be documented

A FedRAMP authorized cloud service brings genuine value to a contractor. The provider has been assessed on controls covering its facilities, its platform operations, and the services it runs, and a contractor using that service can inherit the portion of a control the provider fully implements. Physical security of a data center you never enter is the clearest example: that is the provider’s control to implement and prove.

Inheritance only counts when it is specific. For each NIST SP 800-171 practice that touches your cloud environment, you should be able to say which part the provider implements, which part you implement, and which part is shared. Providers publish this as a customer responsibility matrix or shared-responsibility documentation. If your System Security Plan simply says “inherited from the cloud provider” without naming the control, the service, and the boundary, an assessor has nothing to test and will treat the claim as unsupported.

There is also a threshold question before inheritance matters at all: is the service itself authorized at the level your work requires? For CUI cloud hosting under DFARS 7012, the cloud offering needs to meet the security requirements equivalent to the FedRAMP Moderate baseline, and the way you use it has to stay inside the authorized service and boundary. A marketing claim of “FedRAMP-aligned” or “FedRAMP-ready” is not an authorization, and it does not support inheritance.

The shared-responsibility split, in practice

Exact splits vary by service, but the pattern across Microsoft 365 GCC, GCC High, and managed hosting environments is consistent enough to plan around.

Who covers what

  • Typically the provider’s: physical facility security, host and platform patching for services the provider operates, the underlying network infrastructure, and availability of the platform itself.
  • Typically yours: who gets an account and what it can reach, multi-factor authentication enforcement, conditional access and device rules, how CUI is shared and with whom, retention and legal hold settings, review of audit logs for your tenant, user training, and your incident response plan and reporting.
  • Typically shared: configuration of security features the provider supplies but you must turn on and set correctly, monitoring and alerting, backup scope and restore testing, and keeping an inventory of which services actually hold CUI.
Inheritance is not abdication. You can inherit a control’s implementation. You cannot inherit away accountability for proving it.

The shared category is where findings concentrate. A platform can offer logging, encryption, and access controls of exactly the right standard, and a contractor can still fail the practice because no one enabled the feature, set the retention period, or assigned anyone to review the output. The control existed. It was never implemented in that tenant.

Where contractors get this wrong

Four mistakes account for most cloud compliance surprises we see.

  • Assuming commercial equals government. A commercial Microsoft 365 tenant is not Microsoft 365 GCC, and neither is it GCC High. They differ in authorization, in where data is stored and who can access it, and in which workloads they support. Contractors handling ITAR data, or CUI that their contract and flow-down language place in GCC High, cannot settle that question with a commercial tenant and a hopeful reading.
  • Treating email as out of scope. CUI arrives by email, gets discussed in Teams, and gets stored in file shares. If the cloud service holding your mail and files is outside your compliant boundary, your boundary is not where your SSP says it is.
  • Forgetting the 72-hour clock. DFARS 7012 incident reporting is your obligation, on a short clock, and it starts at discovery, not at the end of your investigation. Your provider’s support queue is not a reporting channel to DoD. Your plan needs named people, a decision path that works on a weekend, and advance clarity about what forensic data your provider will preserve and hand over, and how fast.
  • Skipping flow-down in the cloud. If a subcontractor stores or processes CUI in its own cloud tenant, its tenant is part of your compliance picture. Confirm in writing which service it uses, whether that service is authorized, and what evidence it can produce. Verbal assurance is not flow-down, in the cloud or anywhere else.

Match the platform to the contract, not to habit

The practical question is not “which cloud is best” but “which cloud does this contract require, for this data.” Read the contract and any flow-down language first: what categories of CUI are involved, whether ITAR applies, and whether the prime has named a specific environment. Then match it: Microsoft 365 GCC serves many contractors handling CUI under standard DFARS terms, GCC High is the environment built for the more demanding cases including ITAR, and managed CUI cloud hosting fits workloads that do not belong in a productivity tenant at all.

Buying above the requirement wastes money. Buying below it creates a migration in the middle of performance, which is the most expensive and disruptive time to move. Getting the match right at the start, and documenting why, is a compliance decision your future assessor will thank you for.

Document it like an assessor will read it, because one will

Close the loop in writing. Your SSP should describe the cloud boundary, name each service in scope, and state control by control what is inherited, what is yours, and what is shared, tied to the provider’s responsibility documentation. Keep the provider’s authorization evidence on file, review the split whenever you add a service or change a configuration, and test the parts that are yours: an access review, a log review, a restore, and a tabletop run of the 72-hour reporting path.

DFARS 7012 compliance in the cloud is achievable, and the right FedRAMP authorized cloud genuinely does carry part of the load. The contractors who hold up are the ones who can draw the line precisely: this is what our provider covers, this is what stays ours, and here is the evidence for both.

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions.

Where does your shared-responsibility line actually fall?

NeoSystems ISG is a managed IT, hosting, and cybersecurity provider built for government contractors. We will map your cloud inheritance, your remaining controls, and your evidence the way an assessor will.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

NeoSystems ISG · UEI K5S3DCMK6SJ4 · CAGE 332H1

← Back to Blog

Cybersecurity · Industry Developments

Government Contractor Cybersecurity After the CMMC Phase 2 Pause: What Did Not Pause

Government contractor cybersecurity did not pause when CMMC Phase 2 did. What the suspension changed, what DFARS, SPRS, CISA, and new supply-chain orders still require, and what to do before year end.

Federal building at dusk connected by gold network lines to a security operations center with a shield emblem

Government contractor cybersecurity did not pause this summer, even though one headline made it sound that way. On July 13, 2026, the Department suspended the CMMC Phase 2 transition, the step that would have made third-party Level 2 certification by a C3PAO a condition of award for most contracts involving Controlled Unclassified Information starting November 10, 2026. Revision 3 of DARS Class Deviation 2026-O0025, issued September 3, 2026, wrote that suspension into the contract language. No replacement Phase 2 start date has been announced.

That is a real change, and it matters for planning and budgets. It is not a holiday. Almost everything underneath Phase 2 stayed in force, and October brought fresh reminders, from CISA’s exploited-vulnerability deadlines to new supply-chain orders, that the operating obligations never stopped. Contractors who read “paused” as “optional” are building risk into contracts they already hold.

What the suspension actually changed

Phase 2 was the certification layer. While it is suspended, CMMC Level 1 and Level 2 requirements in new and existing solicitations and contracts may be satisfied through self-assessment, and whether a specific CMMC level is required before the clause becomes automatic is decided case by case by the program office. The third-party assessment, as a universal gate on award, is what moved.

That is the whole list. A suspension of one verification mechanism is not a suspension of the underlying security requirements, and the Department said so at the time: Phase 1 self-assessment requirements remain firmly in place.

What did not pause

  • DFARS 252.204-7012. The safeguarding obligation for covered defense information, in practice implementing NIST SP 800-171, and DFARS incident reporting within 72 hours of discovery are unchanged. They apply on every contract that touches covered defense information, they flow down to subcontractors, and no CMMC announcement touches them.
  • SPRS and affirmation. Your self-assessment still has to be done, scored honestly, posted in SPRS, and affirmed by a senior official on the required cycle. A score that is stale, or an affirmation that has lapsed, breaks your “current” status whether or not a C3PAO was ever going to visit. “We posted a score once” was never the same as being current, and it still is not.
  • The government’s own assessments. The Department retains authority to conduct its own NIST SP 800-171 assessments. Losing the C3PAO gate did not remove scrutiny; it shifted more of it back to self-attestation, which a government assessment, or a prime’s review, can still test.
  • Your primes. Primes were setting their own supplier deadlines for Level 2 readiness before the suspension, driven by their own risk and their own flow-down exposure. A prime’s internal deadline does not suspend just because the Department’s did. If your largest customer asks for evidence this quarter, “Phase 2 is paused” is not an answer that keeps the work.
The pause moved who checks your work, and when. It did not lower the standard the work is checked against.

October made the point again: patching is not a compliance project, it is operations

On October 8, 2026, CISA added five vulnerabilities to its Known Exploited Vulnerabilities catalog and gave federal agencies until October 11, three days, to patch or decommission affected systems. The five flaws affected ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. Four of the five dated from 2015 to 2021, with patches available for years, and CISA attributed the active exploitation to China-linked actors associated with Integrity Technology Group in a joint advisory from seven nations. Four of the five also carried a forensic triage requirement: patching alone was not treated as proof that earlier access was gone.

CISA kept adding exploited flaws through October, with further catalog entries on October 20 carrying federal due dates as early as October 23. Those deadlines bind federal agencies directly, not contractors. Read them anyway. They describe the threat your contracts assume you are defending against: state actors working old, known, patchable flaws at scale because so many environments never closed them. A contractor whose patching rhythm is quarterly, and whose asset inventory is a spreadsheet nobody trusts, does not have a CMMC problem first. It has an operations problem that any assessment, incident, or prime review will find.

The supply chain moved in October, too

Two more October developments belong on a compliance lead’s desk, because both turn vendor choices into contract terms.

A Department of Homeland Security order under the Federal Acquisition Supply Chain Security Act, published in the Federal Register on October 20, 2026, requires civilian agencies to remove DeepSeek products and bars new purchases. For contractors, the mechanics run through FAR clause 52.204-30: if that clause is in your contract, you may not provide or use the covered product in performing it, and primes must flow that restriction down. Whether a named tool is in your environment is now a question you need an inventory to answer.

Separately, GSA’s data-safeguarding terms for contractor use of large language models took effect October 19, 2026. The direction is consistent: government data processed by an LLM may not be treated as ordinary commercial training material, and incident reporting, audit logging, and subcontractor flow-down follow the data into the AI supply chain. If your teams use AI tools on contract work and no one has mapped which tools touch government data, that map is now contract hygiene, not an IT side project. This is supply chain risk management in its practical form: know what you use, know what it touches, and be able to prove both.

What to do before year end

None of this requires panic. It requires a short, honest list, worked in order.

The no-pause checklist

  • Open SPRS and confirm your score and affirmation are current, not just present, and that the score matches your SSP.
  • Read the clauses in your actual contracts and modifications. The 2026 deviation changed some clause numbers in new instruments; legacy obligations in existing contracts do not amend themselves.
  • Run your asset inventory against CISA’s KEV catalog. Close exploited flaws first, and where triage is called for, check for prior compromise instead of assuming a patch erases it.
  • Inventory vendors, cloud services, and AI tools that touch contract data. Confirm flow-down language reaches the subcontractors and service providers who handle CUI or government data.
  • Rehearse DFARS incident reporting once: who discovers, who decides, who reports, inside 72 hours, on a weekend. A plan no one has walked through is a hope, not a plan.
  • Keep closing POA&M items in risk order. Self-assessment raises, not lowers, the value of a credible, dated remediation record.

Federal contractor compliance in this period rewards the same posture it always has: a truthful scope, controls that actually operate, evidence that is current, and an incident path that works under time pressure. The contractors using the pause well are treating it as schedule relief for one assessment step, and spending the time on the fundamentals that every other mechanism, self-assessment, government assessment, prime review, or an actual incident, will still test.

Government contractor cybersecurity was never really about the assessment date. It is about whether your environment, today, matches what your contracts say it is. That question did not pause.

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions.

Not sure what the pause changed for your contracts?

NeoSystems ISG is a managed IT, hosting, and cybersecurity provider built for government contractors. We will review your SPRS status, your patching and vendor picture, and your 72-hour reporting path the way a prime or an assessor will.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

NeoSystems ISG · UEI K5S3DCMK6SJ4 · CAGE 332H1

← Back to Blog

CMMC · Compliance

CMMC 2.0 Requirements: Flow-Down to Subcontractors — What Primes Must Send Down and Subs Must Prove

CMMC 2.0 requirements flow down to subcontractors who handle CUI. What primes must send down in writing, what subs must prove, and how to build a flow-down file that holds up.

Prime contractor headquarters at dusk connected by gold network lines to subcontractor facilities with a shield emblem

CMMC 2.0 requirements do not stop at the prime contractor. When a subcontractor stores, processes, or transmits Controlled Unclassified Information, the obligations follow the data — and both sides of that handoff get judged on whether they can prove it happened correctly. Primes that treat flow-down as a boilerplate clause, and subs that treat it as a signature exercise, discover the gap at the worst moment: during source selection, a prime review, or an assessment.

Getting flow-down right is not complicated, but it is specific. The clause has to name the right level, the sub has to know exactly which systems are in scope, and the evidence has to exist before anyone asks for it. That discipline is the core of CMMC compliance for the supply chain, and it is where defense contractor cybersecurity succeeds or fails in practice.

What the rules actually require to flow down

Under DFARS 252.204-7012, a contractor must flow the safeguarding and incident-reporting requirements down to subcontractors that will handle covered defense information, and must require them to do the same further down the chain. DFARS 252.204-7021 and the CMMC program rule add the certification layer: when CMMC applies to the prime contract, the prime must ensure subcontractors hold the CMMC status required for the information they will handle — no higher than necessary, and no lower than the work demands.

Three distinctions decide whether that language helps or hurts:

  • FCI is not CUI. A subcontract that only involves Federal Contract Information calls for CMMC Level 1. A subcontract that involves CUI calls for Level 2. Flowing Level 2 down to every supplier, including vendors who never touch CUI, wastes money and creates friction primes do not need. Flowing Level 1 language to a sub who will receive CUI leaves the prime exposed.
  • The clause is not the conversation. Inserting DFARS language into a purchase order satisfies a paperwork step. It does not tell the sub which drawings, specifications, or emails are CUI, which systems may receive them, or who to call after an incident. Subs cannot protect what they cannot identify.
  • External providers count. Cloud services, managed service providers, and other external service providers that store, process, or transmit CUI for a subcontractor are part of that subcontractor’s assessment boundary picture. If a sub handles CUI in a commercial cloud with no plan for how that provider fits the requirements, the flow-down problem has simply moved one layer further away.
Flow-down is not forwarding a clause. It is transferring a defined obligation, to a defined scope, with a way to verify it was met.

What a prime should send down — in writing

A defensible flow-down package is short, written, and kept on file for each in-scope subcontractor. It should cover five things.

First, name the level and the standard: the CMMC level required for the work, that NIST SP 800-171 is the practice set behind Level 2, and the date by which the sub must be ready or certified, as applicable to the contract. Second, define the information: categories or markings of CUI the sub will receive, how it will be delivered, and what the sub may not do with it — no personal accounts, no unapproved cloud storage, no further sharing without consent.

Third, name the reporting path. Under DFARS 7012 the 72-hour rapid-reporting clock starts at discovery, and a prime cannot meet its own obligation if a sub sits on an incident over a weekend. The subcontract should state who the sub notifies, how fast, and what information travels with that notice. Fourth, state the evidence the prime will ask for and when: a current SPRS score for Level 2 work, a System Security Plan summary or attestation, POA&M status where relevant, and, when certification is required, the certificate or assessment result. Fifth, preserve the right to verify — a review, a questionnaire with follow-up, or an on-site or virtual evidence check proportionate to the risk of the work.

None of this requires a prime to run a subcontractor’s IT. It requires the prime to be able to show, subcontractor by subcontractor, what was required, what was communicated, and what was received back.

What a sub should be able to prove — before the prime asks

Subcontractors are often surprised less by the requirements than by the request arriving with a deadline. The subs who keep work are the ones who can answer a flow-down review in days, not months. That answer rests on the same foundation as any Level 2 readiness effort, organized so someone outside the company can follow it.

Start with scope. Which systems, people, and locations handle CUI from this prime — and which do not? A one-page scoping statement and data-flow description, tied to the SSP, prevents the most common review failure: CUI found in systems the sub described as out of scope. Next, the SSP itself: how each applicable NIST SP 800-171 practice is implemented, by which system, with evidence a reviewer can sample. Then SPRS: a score calculated honestly from what is implemented today, posted and current, with the senior-official affirmation kept on its cycle. Where gaps remain, a POA&M that names the practice, the risk, the fix, the owner, and a dated milestone — not a list of intentions.

Finally, the operating proof primes increasingly ask for: multi-factor authentication enforced for CUI access, centralized logging that is actually reviewed, patching records, access reviews, incident-response roles with a tested reporting path, and training records for the people who handle CUI. If your CUI lives in Microsoft 365, be able to say whether it is GCC or GCC High, why that choice fits the contract, and which controls you inherit from the platform versus operate yourself.

Where flow-down breaks — and how to fix it early

The same failures appear across the supply chain. A prime flows the clause but never inventories which subs actually receive CUI, so half its review effort lands on vendors with no CUI and none lands on the machine shop that gets drawings weekly. A sub signs a compliance representation to win the award, then starts the readiness work — backwards, and visible the moment evidence is requested. A sub-subcontractor or cloud tool is added mid-performance with no scope check, quietly expanding the boundary. Or an incident happens at the sub and the prime learns about it from someone else, after the reporting window has narrowed.

The fix is a rhythm, not a heroic project. Primes should maintain a living flow-down register: subcontractor, CUI yes or no, level required, evidence received, evidence due date, and open gaps. Subs should review that same picture from their side whenever a new contract, customer, tool, or facility touches CUI. Both sides should revisit it at least annually and at every major change, because CMMC compliance is a current-status obligation, not a one-time filing.

The flow-down file — for primes and subs

  • Contract and subcontract clauses identified, with the CMMC level required for the actual information involved.
  • Written notice to each in-scope sub: level, CUI categories, delivery method, handling limits, and incident notification path.
  • Evidence on file per sub: SPRS status, SSP or attestation, POA&M status, and certification result where required.
  • A register with owners and due dates, reviewed at award, at major changes, and at least annually.
  • External service providers inventoried — every cloud or managed provider that touches CUI named and accounted for.

When that file exists, a prime review becomes a short administrative step instead of a scramble, and a sub’s CMMC compliance story becomes something it can show rather than assert. In a market where primes must manage their own risk, that difference decides who stays on the team.

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions.

Need your flow-down picture reviewed?

NeoSystems ISG is a managed IT, hosting, Microsoft cybersecurity, and CMMC compliance provider built for government contractors: managed hosting, Microsoft 365 GCC and GCC High, cybersecurity, and CMMC compliance support.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

NeoSystems ISG · UEI K5S3DCMK6SJ4 · CAGE 332H1

← Back to Blog

Cloud & Hosting · CUI Hosting

CUI Cloud Hosting: When a Productivity Tenant Is Not the Right Home for CUI

CUI cloud hosting is for workloads a productivity tenant handles poorly: large CUI files, ITAR data, and line-of-business applications. How to choose between Microsoft 365 GCC, GCC High, and managed hosting without expanding your boundary.

Secure cloud data center at dusk in navy and gold with a gold boundary line around a hosted server enclave

CUI cloud hosting answers a question Microsoft 365 alone cannot: where should Controlled Unclassified Information live when it is not mail, chat, or an office document? Many contractors start with a productivity tenant and assume every workload belongs there. Then engineering files grow, a line-of-business application needs a server, or ITAR data arrives, and the tenant becomes the wrong home for work it was never built to hold.

The choice is not Microsoft 365 GCC or GCC High versus hosting in the abstract. It is workload by workload: which system holds which CUI, under which authorization, inside which boundary you can describe in your System Security Plan and defend to an assessor. Getting that placement right keeps your boundary small. Getting it wrong expands your boundary every time someone uploads a file to the convenient place instead of the approved one.

Start with the workload, not the platform

Productivity tenants do productivity work well. Microsoft 365 GCC serves many contractors handling CUI in email, Teams, and SharePoint under standard DFARS terms, and GCC High is the environment built for more demanding cases, including ITAR and CUI that contract or flow-down language places there. If your CUI is mostly documents, messages, and collaboration, a correctly chosen and correctly configured tenant may be the whole answer.

Other workloads fit poorly in a tenant. Large CAD and engineering files teams need to open and revise at speed. Applications that require a server, a database, or operating-system controls the tenant does not offer. File shares with years of program history that cannot move to SharePoint without breaking how people work. Workloads that should be isolated from everyday email and browsing.

Naming those workloads honestly is the first decision. Force every workload into the tenant and people route around it, creating shadow copies outside the boundary. Place each workload deliberately and the boundary is one you can actually enforce.

What managed CUI cloud hosting adds

Managed CUI cloud hosting places those non-productivity workloads in a separate, controlled environment: servers and storage inside a defined boundary, accessed by named users, logged, patched, and backed up under the same discipline you apply to the rest of your CUI environment. The value is not that hosting is inherently more secure than a tenant. The value is fit and control: the workload runs where its requirements can actually be met, and it stays inside scope instead of spreading.

Three conditions make hosting the stronger choice. First, the application requires it: the vendor supports a server deployment, not a tenant integration, or the workload needs compute and storage shapes a productivity suite does not provide. Second, the data requires it: ITAR data, large volumes of CUI, or program files that need tighter access segmentation than shared collaboration spaces allow. Third, the boundary requires it: keeping a high-risk workload separate lets your tenant stay focused on collaboration, and your assessment scope stays describable in a page instead of sprawling across every tool the company touches.

Place each CUI workload where its requirements can actually be met, and write down why. A boundary drawn by fit holds up. A boundary drawn by habit does not.

The authorization question applies here too

Hosting does not waive the authorization test. For CUI cloud hosting under DFARS 252.204-7012, the underlying cloud service needs to meet security requirements equivalent to the FedRAMP Moderate baseline, and the way you use it must stay inside the authorized service and boundary. A FedRAMP authorized cloud underneath a managed environment is the foundation, not the whole structure: the managed layer above it, identity, configuration, logging, and incident response, is implemented by you and your provider and must be documented control by control.

Apply the same skepticism you would to any platform claim. “Hosted in a compliant data center” describes a building. It does not describe your servers, your access controls, or your evidence. Ask which service is authorized, at what level, what the provider implements above that service, and what remains yours. Those answers belong in your SSP, tied to a responsibility matrix, not in a sales deck.

ITAR sharpens the question further. If a workload involves ITAR data, confirm that the environment, the people who can administer it, and the support paths around it fit the restrictions that data carries, before the data moves. Retrofitting ITAR controls around data already in the wrong environment is far harder than placing it correctly at the start.

Keep GCC, GCC High, and hosting as one boundary picture

Most contractors who need hosting run both: Microsoft 365 GCC or GCC High for mail and collaboration, and managed hosting for applications and file workloads that do not belong there. That hybrid only works when drawn as one picture. Which identities exist in each environment, with the same multi-factor discipline? How does CUI move between them, and is that movement allowed, logged, and limited? Which environment is the system of record for each CUI category, so staff are not keeping live copies in both? Who reports an incident that touches both, and how fast does it reach the person who owns the 72-hour DFARS clock?

Before you place a workload in CUI cloud hosting

  • Name the workload and the CUI it holds, including whether ITAR applies, and who uses it.
  • Confirm the underlying service is a FedRAMP authorized cloud offering at the level your contract requires, and keep that evidence on file.
  • Write the responsibility split: patching, logging and review, backups and restore testing, access reviews, and incident response, each with a named owner.
  • Define how CUI moves between the hosted environment, Microsoft 365 GCC or GCC High, and anywhere else, and what movement is prohibited.
  • Describe the whole picture in the SSP: boundary, services in scope, and what is inherited, shared, and yours.

When those answers exist, a hybrid environment is not complexity for its own sake. It is a smaller, clearer boundary than forcing unlike workloads into one tool, and assessors can follow it.

Decide by contract and data, then document the decision

Read the contract and flow-down language first: what CUI categories are involved, whether ITAR applies, and whether a prime has named a specific environment. Match each workload to that requirement. Productivity work goes to the tenant that fits, GCC or GCC High. Server, application, and heavy file workloads go to managed hosting built on an authorized foundation. Nothing goes to a commercial tenant or a personal account because it was convenient on a deadline.

Then write the decision down while it is still a decision, not a reconstruction. A short placement record per workload, workload, data, environment, reason, and owner, becomes some of the most useful evidence you own when a prime or an assessor asks why your boundary looks the way it does.

CUI cloud hosting is not a replacement for Microsoft 365 GCC or GCC High, and it is not an upgrade to sell yourself. It is the other half of a complete placement picture, for the CUI that was never mail or a document in the first place.

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions.

Not sure where a workload belongs?

NeoSystems ISG is a managed IT, hosting, Microsoft cybersecurity, and CMMC compliance provider built for government contractors: managed hosting, Microsoft 365 GCC and GCC High, cybersecurity, and CMMC compliance support.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

NeoSystems ISG · UEI K5S3DCMK6SJ4 · CAGE 332H1

← Back to Blog

Cybersecurity · Incident Response

DFARS Incident Reporting: Why This Week's KEV Deadlines Start Your 72-Hour Clock Before a Breach Is Confirmed

DFARS incident reporting gives contractors 72 hours from discovery to report to DoD. This week's Cisco ASA/FTD and PHP KEV deadlines show why discovery, triage, and evidence preservation must start before compromise is confirmed.

Security operations center at dusk monitoring an edge firewall and VPN gateway in navy and gold with a shield emblem and clock motif

DFARS incident reporting gives a contractor 72 hours from discovery of a cyber incident to report it to the Department of Defense. That clock does not wait for certainty. This week made the point twice in three days: CISA set an October 29 federal remediation deadline for two exploited PHP flaws, then added an actively exploited Cisco ASA and FTD VPN flaw on October 29 with a federal deadline of November 1 and no workaround. For government contractor cybersecurity, the lesson is not just patch faster. It is that discovery, triage, and the reporting decision have to run in parallel, because by the time compromise is proved, the clock may already be spent.

A Known Exploited Vulnerabilities listing is not a breach notice for your company. It does not by itself mean you must file a report. What it does mean is that a flaw in a product you may run is being exploited in the wild, and a contractor who finds that flaw in its own CUI boundary now has a discovery problem to work honestly and quickly: are we affected, were we exploited, and does what we found meet the reporting threshold in our contracts?

Two deadlines in one week: PHP, then your VPN edge

On October 26, CISA added both PHP2Shell flaws, CVE-2026-109618 and CVE-2026-109619, to the KEV catalog and set a remediation due date of October 29 for federal civilian agencies under Binding Operational Directive 26-04. Both flaws carry a CVSS score of 9.2. Fixed PHP versions, 8.5.12, 8.4.27, 8.3.36, and 8.2.35, were released October 21. The catalog entries flag both flaws for forensic triage, require mitigations in line with vendor instructions, and name discontinuing use as the fallback if mitigations are unavailable. Reporting summarized by the catalog noted honeypot activity on October 24 consistent with exploitation, with attackers running shell commands through the flaw.

Then the edge itself. Cisco disclosed on October 28 that a flaw in the Remote Access SSL VPN service of its Secure Firewall ASA and FTD software was being actively exploited, and CISA added it to the KEV catalog the next day, October 29. The flaw, CVE-2026-76418, carries a CVSS score of 8.6. Cisco describes it as a logic error when secondary authentication is configured on a tunnel group: an unauthenticated remote attacker can send a crafted request and force the device to reload, a denial-of-service condition. Cisco lists fixed releases and states there is no workaround; disabling secondary authentication on affected tunnel groups can reduce exposure, but it removes a layer of authentication rather than closing the flaw. CISA’s federal remediation date is November 1.

Neither deadline legally binds a contractor the way it binds a federal civilian agency. Work to the federal dates anyway. They are the government’s own measure of how urgent exploited means, and a prime, an assessor, or an incident reviewer will judge your timeline against them.

Where the 72-hour clock actually starts

Under DFARS 252.204-7012, a contractor that discovers a cyber incident affecting covered defense information, or systems that hold it, must rapidly report it within 72 hours, preserve images and relevant data, and cooperate with follow-on review. The hard part in practice is rarely the form. It is the word discovery.

Discovery is not the moment a report is confirmed complete. It is the moment your team has information that a reasonable review would treat as an incident: an exploited flaw confirmed on an in-scope system, logs showing the pattern the vendor or CISA described, a device reloading in a way that matches the attack, credentials or files out of place after exposure. Contractors lose the clock in the gap between the first engineer seeing something and anyone deciding it counts. Fix that gap in advance: name who can declare discovery, who owns the report, and what evidence gets preserved before patching overwrites it.

Patching and reporting are not alternatives. For the PHP flaws, CISA’s own triage flag says patching alone does not prove earlier access is gone, so hunt first, or at least preserve first: PHP processes launching shells, new files in web roots, and signs of disclosure, looking back over the exposure window. For the Cisco flaw, preserve device logs and configuration before the upgrade and the next reload, and note exactly which tunnel groups had secondary authentication configured, because that condition defines whether you were in the affected set at all.

The 72-hour clock rewards the contractor who preserved evidence and made the call early. It punishes the one who patched first, discussed it for two days, and then tried to reconstruct what happened.

The third story this week: who, or what, holds your admin access

A separate report this week belongs in the same conversation, handled carefully because it is disputed. WIRED reported on October 29, in an investigation summarized in subsequent coverage, that an Accenture employee allegedly gave a personal AI coding agent administrative access to a secure Defense Department environment holding CUI, that the agent operated for about two months, and that credentials and network details appeared to have been sent to an outside website. Accenture told WIRED the allegations were thoroughly and independently investigated and found to be without merit, and that it met its legal and contractual duties. The Pentagon declined to discuss its network status. Treat the specifics as alleged and disputed, not established.

The governance question underneath it is not disputed at all, and it applies whether or not any part of that account proves true. AI coding agents, automation tools, and personal accounts are now part of supply chain risk management: if a tool can hold credentials, act under an employee’s identity, write and deploy code, or send data outside your boundary, it belongs in your inventory, your access review, and your incident plan. Short-lived credentials, narrow permissions, no personal accounts on contract systems, and logs that distinguish a person’s actions from an agent acting for them are not AI policy extras. On a CUI contract, they are federal contractor compliance.

A weekend-ready checklist for KEV weeks

When a KEV deadline lands on your stack

  • Inventory first: do we run the product, in the affected configuration, anywhere in or near the CUI boundary? For Cisco, that means SSL VPN enabled with secondary authentication on a tunnel group. For PHP, internet-facing and mod_php deployments first.
  • Patch to the vendor’s fixed release by the federal date, restart the service so the fixed build actually serves traffic, and verify the running version, not just the installed package.
  • Preserve before you patch: logs, configurations, and images you would need for DFARS incident reporting and a later review.
  • Run the triage the catalog calls for. Where exploitation is confirmed on an in-scope system, declare discovery, start the 72-hour clock, and report. Do not wait for a complete root cause.
  • Record the negative results too: systems checked, versions found, and systems taken offline instead of patched, with dates. A documented not-affected finding is evidence.
  • Review agent and tool access the same week: personal accounts, standing admin rights, and any automation that can act with an employee’s credentials.

None of this requires a large security team. It requires an inventory you trust, a patching rhythm measured in days, an evidence habit, and a reporting decision that does not need a meeting to start.

Government contractor cybersecurity is tested on weeks like this one, not on quiet ones. Two exploited flaws, two three-day federal clocks, and one disputed report about who held admin access all point to the same standard: know what you run, know who and what can act in it, and be able to prove what you did, and when, inside 72 hours.

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions.

Need your incident path tested before a KEV week tests it for you?

NeoSystems ISG is a managed IT, hosting, Microsoft cybersecurity, and CMMC compliance provider built for government contractors: managed hosting, Microsoft 365 GCC and GCC High, cybersecurity, and CMMC compliance support.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

NeoSystems ISG · UEI K5S3DCMK6SJ4 · CAGE 332H1

← Back to Blog

CMMC · Compliance Operations

CMMC Compliance Is a Calendar, Not a Project: The Maintenance Rhythm That Keeps Your Status Valid

A Level 2 certification is valid for three years, but only while the affirmations are made, the POA&M closes on time, and the assessed environment stays the assessed environment. CMMC compliance after assessment day is a calendar — here is the one to run.

Compliance operations wall at dusk with a gold calendar grid and checklist board, shield emblem, and federal office building in navy and gold

CMMC compliance is usually treated as a project: build the enclave, write the System Security Plan, pass the assessment, file the certificate. The project ends. The obligations do not. Under CMMC 2.0 requirements, a Level 2 certification stays valid only while a senior official affirms it every year, POA&M items close inside a fixed window, and the environment that was assessed stays recognizably the environment that exists. Contractors who budget for the assessment and not the maintenance discover the difference when a prime asks for a current affirmation and nobody can say when the last one was made.

The good news is that the maintenance load is predictable. Almost everything CMMC asks for after assessment day falls on a known date, a known interval, or a known event. Put all three on one calendar, assign an owner to each line, and defense contractor cybersecurity stops being a recurring emergency and becomes a routine.

The dates that are already fixed

Three obligations carry hard dates, and none of them moves because someone was busy.

The annual affirmation. A Level 2 certification is valid for three years, but it is not self-sustaining. A senior official of the company must affirm compliance in SPRS every year — within a year of the certification and on each anniversary cycle after it. Level 1 has the same shape: an annual self-assessment and an annual affirmation. Miss the affirmation and the status a prime sees is no longer the status you earned, whatever the certificate on the wall says.

The POA&M clock. Where an assessment leaves a conditional status, the permitted POA&M items must close within 180 days, with a follow-up closeout assessment to confirm it. That window is short enough that it cannot start with a planning meeting in month four. Every POA&M item needs an owner, a funded fix, and a milestone date the week the assessment report lands — and only certain lower-weight practices are eligible for a POA&M at all, which is why the plan written before the assessment matters more than the plan written after it.

The SSP and score refresh. The System Security Plan and the SPRS score describe the environment as assessed. Both go stale by design: systems change, people rotate, scores change as practices are implemented or slip. An annual SSP review is the minimum discipline; any quarter with real change in it deserves one sooner. A score that no longer matches the environment is worse than a lower honest score, because the affirmation behind it is what a senior official signs.

An assessment proves what your environment was on one week in one year. The affirmation is a senior official stating, every year after, that it is still true.

The events that should trigger work between the dates

Calendar dates catch slow drift. Events catch sudden change, and CMMC compliance fails on events more often than on anniversaries. Four triggers deserve a standing rule in any contractor’s change process.

A new system, cloud service, or managed provider touches the CUI boundary: is it in scope, is it in the SSP, does the provider meet the requirements the contract flows down, and does the SPRS picture change? A new contract or new CUI category arrives: the enclave sized for one customer’s drawings may not be the right answer for another’s technical data, and the scope decision belongs at award, not at first delivery. People change roles: the administrator who leaves, the new hire who gets CUI access before training is recorded, the departing employee whose accounts linger. And an incident or near-miss occurs: the response, the reporting decision under DFARS 7012’s 72-hour clock, and the lessons folded back into the SSP are all evidence of whether the program is alive.

None of these requires an assessor’s permission. All of them require someone to ask the scope question at the moment of change rather than at the next annual review — which is exactly why the trigger list belongs inside the ordinary change ticket, not in a compliance binder nobody opens.

The quarterly rhythm underneath

Between the annual events sits the operating cadence the 800-171 practices already assume: vulnerability scanning and patching on a defined cycle with records kept, log review that actually happens and can be shown, access reviews that remove what people no longer need, backup tests, and training kept current for everyone who touches CUI. Assessors sample this evidence across the whole period since the last look, not just the month before they arrive. A contractor running the rhythm quarterly has an evidence file that builds itself. A contractor who reconstructs it annually has a project again — the expensive kind, under deadline, with a prime waiting on the answer.

This is also where the maintenance picture connects to the rest of the business. The same calendar that holds the affirmation date should hold the flow-down reviews for subcontractors, the ESP inventory check, and the incident-response tabletop. One owner, one calendar, one quarterly review where leadership sees open POA&M items, upcoming affirmations, and scope changes in a single page.

The 12-month CMMC maintenance calendar

  • Affirmation date on the calendar with a 60-day warning: senior official, SPRS, signed and recorded.
  • POA&M milestones tracked from assessment day, all items closed inside 180 days, closeout assessment scheduled.
  • SSP and data-flow review at least annually, and after any scope-changing event.
  • SPRS score recalculated whenever implementation changes — before the affirmation, not after a prime asks.
  • Quarterly: access review, scan and patch records, log-review evidence, backup test, training roster check.
  • Standing change triggers: new system or provider, new contract or CUI type, role changes, incident — each one asks the scope question.
  • Annual: incident-response tabletop, subcontractor flow-down evidence refresh, ESP inventory review.

What this costs versus what it saves

The honest comparison is not maintenance versus nothing. It is maintenance versus re-assessment risk: a lapsed affirmation, a conditional status that expires unclosed, or a certification that no longer describes the environment are all findings a prime can act on immediately, and re-work under contract pressure costs more than the calendar ever will. Primes are managing their own exposure, and the subcontractor who can produce a current affirmation, a closed POA&M, and a change log that matches the SSP is the subcontractor who stays easy to keep.

CMMC compliance, done this way, is unglamorous: dates met, evidence filed, questions asked at the moment of change. That is the point. The contractors who keep their status valid for the full three years are not the ones who ran the biggest assessment project. They are the ones who put the obligations on a calendar and treated it like any other commitment the business has made.

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions.

Not sure which of your CMMC dates are already at risk?

NeoSystems ISG is a managed IT, hosting, Microsoft cybersecurity, and CMMC compliance provider built for government contractors: managed hosting, Microsoft 365 GCC and GCC High, cybersecurity, and CMMC compliance support.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

NeoSystems ISG · UEI K5S3DCMK6SJ4 · CAGE 332H1

← Back to Blog

FedRAMP & Federal Cloud · Microsoft 365

Microsoft 365 GCC: What You Inherit, What You Must Configure, and What You Still Own

Microsoft 365 GCC gives contractors an authorized foundation, not a finished compliance program. Inheritance is real but partial — here is where Microsoft's half ends, where tenant configuration decides, and what stays yours to prove.

Secure cloud tenant dashboard over a federal office building at dusk, gold boundary lines separating inherited platform controls from tenant configuration controls, shield emblem, in navy and gold

Microsoft 365 GCC is often bought as if the purchase itself were the compliance work. It is not. Microsoft 365 GCC gives a government contractor a FedRAMP authorized cloud foundation for email, files, and collaboration — and then hands the contractor a long list of tenant decisions that determine whether that foundation actually protects Controlled Unclassified Information. Inheritance is real, but it is partial, and an assessor will test the boundary between what Microsoft provides and what your organization configured, documented, and can prove.

That boundary is where most GCC programs succeed or stall. Buy the right tenant, leave sharing open, skip audit settings, and let accounts accumulate, and the authorized platform underneath does not rescue the implementation above it. Configure the tenant deliberately, map what is inherited control by control, and keep evidence as you go, and the same tenant becomes a defensible part of a DFARS 7012 compliance program instead of an expensive assumption.

What you actually inherit

Inheritance means specific controls, implemented by Microsoft inside its authorized boundary, that your System Security Plan can cite rather than rebuild. In Microsoft 365 GCC that typically covers the physical and platform layers: data-center security, the underlying infrastructure, platform patching and hardening Microsoft manages, and service-level capabilities assessed as part of the authorization package. The evidence for those controls lives in Microsoft’s authorization documentation, and your job is to reference it accurately — which service, which authorization, which controls — not to paraphrase a marketing page into your SSP.

Two limits matter. First, inheritance applies only inside the authorized service and the way it was assessed. A feature, add-on, or connected service outside that boundary inherits nothing, however convenient it is. Second, inherited controls do not configure your tenant. Microsoft can operate a secure platform while your sharing settings, guest access, and retention choices still expose the CUI you put on it. Assessors know this, which is why “Microsoft handles that” fails as an answer unless it names the control, the package, and the exact split.

Inheritance is a list, not a feeling. If a control is not named, mapped to the authorization package, and separated from your tenant duties, an assessor will treat it as yours — and unproven.

What tenant configuration decides

The tenant layer is yours, and it is where day-to-day risk lives. Identity comes first: multi-factor authentication enforced for everyone who can reach CUI, conditional access that reflects how your people actually work, privileged accounts separated and tightly held, and prompt removal of access when roles change. A GCC tenant with weak identity settings is not protected by the platform beneath it; the platform faithfully delivers CUI to whoever the tenant says may have it.

Sharing and collaboration settings come next. External sharing in SharePoint and OneDrive, guest access in Teams, and forwarding and connector rules in Exchange decide whether CUI stays inside the boundary you described. Default settings are built for ease of collaboration, not for your contract. Every sharing path that stays open should be open on purpose, limited to named needs, and reviewable — because the data-flow diagram in your SSP and the sharing toggles in your admin center must tell the same story.

Protection and evidence settings complete the picture: sensitivity and retention labels applied where CUI actually lives, data-loss-prevention rules that match your CUI categories, audit logging turned on, retained, and actually reviewed, and alerts routed to someone who acts on them. None of this is exotic. All of it is configuration a contractor must choose, document, and revisit — and none of it is inherited.

What stays yours even in GCC High territory

Moving up does not retire these duties. GCC High raises the environment around the data — it is the tenant built for more demanding cases, including ITAR and stricter contract demands — but the split has the same shape: Microsoft provides the authorized platform, and the contractor still owns identity, sharing, configuration, training, and evidence. Choosing between Microsoft 365 GCC and GCC High is a contract-and-data decision; running either one well is an operations decision, and it does not make itself.

The same applies to the program around the tenant. Your SSP must describe this tenant, your boundary, and your responsibility matrix as implemented, not as licensed. Incident response still runs on your clock: when something happens in the tenant, DFARS 7012’s 72-hour reporting obligation belongs to you, including knowing in advance who reviews the logs, who decides, and who reports. Subcontractor flow-down also stays yours — a supplier with access to your tenant is inside your boundary, whatever their own environment looks like.

The GCC inheritance checklist

  • List every inherited control by name, tied to the authorization package for the exact service you use.
  • Draw the tenant boundary: which services, add-ons, and connected tools are in scope, and which are prohibited for CUI.
  • Baseline identity: MFA enforced, conditional access documented, privileged accounts separated, leavers removed promptly.
  • Set sharing deliberately: external sharing, guest access, and forwarding rules limited, named, and reviewed on a schedule.
  • Turn evidence on before you need it: audit logging retained and reviewed, labels and DLP matched to your CUI categories.
  • Write the responsibility matrix into the SSP and test incident response against the 72-hour DFARS clock.

Prove the split before an assessor asks

The practical test is simple. Pick any control your SSP claims as inherited and produce three things: the authorization evidence that covers it, the tenant setting or process that covers your half, and a recent record showing your half is working — an access review, a log review, a sharing audit. Where any of the three is missing, you have found the work. Contractors who run that test quarterly arrive at assessments with a tenant that matches its paperwork. Contractors who skip it discover the gaps in front of a prime, on the prime’s schedule.

Microsoft 365 GCC is a strong foundation precisely because so much beneath the tenant is assessed and operated at scale. Its value is only realized by the unglamorous work above it: configuration chosen on purpose, a responsibility split written down control by control, and evidence kept while the work happens. That is what turns a licensed tenant into a compliance position you can defend.

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions.

Not sure where your GCC inheritance ends and your tenant duties begin?

NeoSystems ISG is a managed IT, hosting, Microsoft cybersecurity, and CMMC compliance provider built for government contractors: managed hosting, Microsoft 365 GCC and GCC High, cybersecurity, and CMMC compliance support.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

NeoSystems ISG · UEI K5S3DCMK6SJ4 · CAGE 332H1

← Back to Blog

GovCon IT & Cybersecurity · Supply Chain

Supply Chain Risk Management: GSA's New Monitoring Clause Puts Your Suppliers in Your Compliance File

Supply chain risk management is no longer a check at award. GSA's GSAR 552.540-70 and 552.540-71 let the government remove an offeror for supplier risk and act during performance — what to inventory and prove now.

Secure supply chain operations wall at dusk with interconnected supplier nodes linked by gold lines converging on a shield emblem in front of a federal office building, in navy and gold

Supply chain risk management used to sit in the background of a proposal: a representation here, a vendor name there, and then the real work of performance. That position is ending. On July 21, 2026, GSA announced two new provisions as part of Wave 3 of its GSAM/R overhaul that formalize how it evaluates supply chain risk before award and monitors it during performance — and for government contractor cybersecurity, the change matters well beyond a single Schedule contract, because it makes your suppliers part of your compliance file whether you organized them that way or not.

The clauses do not invent a new concern. They write down, in contract language, a practice contractors could previously treat as informal: the government looks at who and what sits behind what you sell it, and it can act on what it finds. Contractors who already inventory their suppliers and keep a mitigation story ready will feel little change. Contractors who cannot answer a supplier question without a week of digging will feel all of it.

What GSA actually changed

The first provision, GSAR 552.540-70, Notice of Evaluation of Supply Chain Risk, applies at evaluation. It provides that the government may consider supply chain risk information during evaluation, and that unacceptable supply chain risks may be grounds to remove an offeror from consideration. That last point deserves emphasis: removal can happen even where supply chain risk is not a stated evaluation criterion in the solicitation. An otherwise competitive offer does not cure a supplier problem the government decides it cannot accept.

The second, GSAR 552.540-71, Supply Chain Risk Monitoring, applies after award, throughout performance. It puts contractors on notice that supply chain risk information will be monitored during the contract, and that the government can take corrective action for risks that cannot be reasonably mitigated. The listed actions are not advisory: removal of the product, service, or solution from the contract, not extending performance, canceling the contract, or termination.

Both provisions use the definition of supply chain risk information in FAR 41.101. Read that definition as the scope of the inquiry: functionality and features, the user environment, foreign ownership, control, or influence, implications for government missions and assets, national security and critical functions, vulnerabilities to federal systems and facilities, market alternatives, and the potential harm from loss, damage, or compromise of what was bought. GSA said the provision and clause will be actively included in forthcoming Federal Supply Schedule refreshes and contract modifications, so for many holders this will arrive not in a new competition but in paperwork for a contract they already hold.

A supplier you cannot describe is a risk you cannot mitigate. Under the new clause, that is no longer an internal gap — it is a contract risk the government can act on.

Why this is not only a GSA problem

Defense contractors will recognize the pattern. DFARS 252.204-7012 already flows CUI protection down the chain, so a subcontractor holding a drawing carries the same NIST SP 800-171 obligations as the prime for that work. NIST SP 800-161 Rev. 1 gives that work its name — cyber supply chain risk management, or C-SCRM — and other agencies are asking for C-SCRM plans and questionnaires in current solicitations. GSA’s move adds a civilian, Schedule-wide version of the same logic: evaluate before award, monitor during performance, and act when a risk cannot be mitigated.

That convergence is the real development for federal contractor compliance. A contractor selling to both defense and civilian agencies no longer has one supply chain story for a CMMC file and a vaguer one for everyone else. The supplier inventory, the critical-component list, and the evidence behind them increasingly have to be the same file, maintained once and usable in either conversation. GovCon IT services providers sit inside that file for many contractors, too — an MSP, a cloud tenant, a help-desk tool, or an AI coding assistant with access to contract systems is a supplier in every sense these clauses care about.

What counts as a supplier now

Think wider than parts and resellers. The chain includes software and SaaS that touch contract data, cloud and hosting providers, MSPs with administrative access, subcontractors and their subcontractors, components and firmware in delivered equipment, and any tool — including automation and AI agents — that can hold credentials, act under an employee’s identity, or move data outside your boundary. If it can affect what the government bought, it belongs in the inventory.

For each entry, the useful record is practical: what the supplier provides, what data or access it touches, where ownership or control sits, what alternatives exist, and what mitigation is already in place. That record turns a government notice — GSA describes a process of notice, mitigation, then corrective action — into a conversation you can have, instead of a deadline met with a spreadsheet built overnight.

The supply chain file to build now

  • Inventory every supplier, product, service, and tool that touches contract performance or contract data, including MSPs, cloud providers, and AI/automation tools.
  • For each, record what it provides, what data or privileged access it holds, and any foreign ownership, control, or influence you know of.
  • Flag single-source and hard-to-replace items, and name a realistic alternative or mitigation for each one.
  • Flow the relevant security and reporting duties down in writing, and collect your subcontractors’ answers before a prime or agency asks.
  • Review the file on a schedule and on change — new supplier, new ownership, new product, or new access — not only at proposal time.
  • Where you find a real risk, prepare a disclosure with a proposed mitigation plan rather than waiting to be asked about it.

What to do before the clause lands in your contract

Start with the solicitations in front of you. Check whether GSAR 552.540-70 is in the offer you are preparing, and whether 552.540-71 is being added at your next refresh or modification. Then run the honest test: if the government identified a concern in your chain tomorrow, could you produce the inventory and mitigation plan from records you already keep? Where the answer is no, that gap — not the clause itself — is the work.

Disclose early where disclosure helps. GSA’s own guidance describes risk identification through investigations, information sharing, audits, and disclosures, and industry guidance on the new clause makes the same practical point: a contractor that surfaces a potential risk together with a credible mitigation plan is in a stronger position than one whose risk is found for it. That does not mean volunteering speculation. It means that a known ownership change, a compromised component, or a supplier that can no longer meet its duties should reach the government through you, with a plan, first.

Supply chain risk management is becoming a performance discipline, not a proposal representation. The contractors who treat it that way — one maintained supplier file, flow-down in writing, mitigation ready before it is demanded — will pass through Schedule refreshes, prime reviews, and agency questions with the same evidence. That is the position worth building now, while the clause is still arriving by modification rather than by corrective action.

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions.

Not sure your supplier file would hold up if GSA, a prime, or an assessor asked tomorrow?

NeoSystems ISG is a managed IT, hosting, Microsoft cybersecurity, and CMMC compliance provider built for government contractors: managed hosting, Microsoft 365 GCC and GCC High, cybersecurity, and CMMC compliance support.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

NeoSystems ISG · UEI K5S3DCMK6SJ4 · CAGE 332H1

← Back to Blog

CMMC Compliance · Assessment Preparation

Defense Contractor Cybersecurity: Building the Evidence File That Passes a CMMC Level 2 Assessment

Defense contractor cybersecurity is judged on evidence, not intentions. How to build the CMMC Level 2 evidence file — by practice, by objective — that a C3PAO can score without a scavenger hunt.

Assessor evidence review table in a secure office at dusk with organized binders, a laptop checklist dashboard and a shield emblem, gold lines tracing documents to control checkmarks in front of a federal office building, in navy and gold

Defense contractor cybersecurity is judged, in the end, on evidence. A contractor can run sound controls, train its people, and protect Controlled Unclassified Information (CUI) carefully — and still fail a CMMC Level 2 assessment because the assessor could not find, date, or trace the proof. CMMC assessment preparation is therefore not mainly a writing exercise in the last month before the C3PAO arrives. It is the discipline of building an evidence file, practice by practice, that shows what was implemented, where, and how the assessor can verify it.

That distinction matters because Level 2 is not scored on confidence. Each of the 110 practices in NIST SP 800-171 Rev. 2 carries assessment objectives, and each objective is met, not met, or not applicable on the evidence presented: documents, records, interviews, and observation. Contractors who understand that scoring model early build a very different file from contractors who assemble a binder of policies and hope the conversation carries the rest.

Start from the objectives, not the policy binder

A policy states intent. An assessment objective asks whether a defined thing happens. For access control, that can mean showing that access is limited to authorized users and processes, that remote sessions are controlled, and that the mechanisms enforcing those limits are actually configured as described. A well-written access control policy supports that showing. It does not replace it.

The practical move is to work backwards from the objectives for each practice. For every practice in scope, list the objective, name the evidence that proves it, name where that evidence lives, and name the person who can speak to it in an interview. Screenshots with dates, configuration exports, ticket and approval records, training rosters, scan results, and log-review records are the currency here — each one tied to the system and the CUI boundary in the System Security Plan (SSP), not floating free as an unnamed file.

When that mapping is done honestly, gaps announce themselves early. A practice may be implemented but leave no record. A record may exist but cover only part of the enclave. A procedure may be documented while the tool that should enforce it was never configured. Finding those gaps in preparation is inexpensive. Finding them in the assessment report is not, and only a narrow set of lower-weight practices is even eligible to sit on a POA&M.

Assessors do not score the environment you describe. They score the environment you can show — objective by objective, with evidence an outsider can follow without your help.

The four kinds of evidence, and why you need more than one

Strong files mix evidence types deliberately, because assessors test the same practice from several directions.

Documentation — the SSP, policies, procedures, data-flow diagrams, and the asset inventory — establishes what the environment claims to be. It must be current, and it must match the other evidence. An SSP that names a decommissioned server or omits a cloud service that holds CUI undermines every practice that depends on scope.

Records are the proof that documented things actually happened: vulnerability scans across the assessment period, patch records, access reviews with removals shown, incident-response tabletop results, backup test results, and media and visitor logs where they apply. One perfect week of records proves one week. Assessors sample across time precisely because NIST 800-171 compliance is an operating condition, not a performance staged for assessment week.

Technical evidence — configuration baselines, multifactor authentication settings, encryption settings, audit-log configuration, and boundary protections — shows the mechanism itself. Where a practice depends on a setting, show the setting in the system of record, exported or captured in a way that identifies the system and the date.

People close the loop. Interviews test whether the staff who operate a control can explain it the same way the documents describe it. The fastest way to prepare is also the simplest: have the people who will be interviewed walk the evidence file themselves, and fix every place where their account and the file disagree — in whichever direction the truth requires.

Keep the file inside the scope you declared

Evidence quality collapses most often at the boundary. The enclave or enterprise scope in the SSP defines which assets are in, which are security protection assets, and which are out — and the evidence has to cover that declared scope completely, no wider and no narrower. A scan report that covers the office network but not the CUI enclave, an access review that omits the hosting provider’s administrators, or a diagram that leaves out the managed service provider with privileged access each creates the same finding: the practice may be met somewhere, but it is not shown to be met where CUI actually lives.

External service providers deserve their own evidence section. For each provider, keep the contract or agreement language that flows the requirements down, the provider’s own compliance standing where relevant, and the shared-responsibility picture that shows which objectives the provider supports and which remain yours. That section does double duty: it is assessment evidence, and it is the same record a prime will ask for when it reviews your flow-down.

The CMMC Level 2 evidence file, by section

  • Current SSP, CUI data-flow diagram, and asset inventory — one declared scope, dated and versioned.
  • An objective-by-objective index: for each of the 110 practices, the evidence, its location, and the interview owner.
  • Records across time, not one week: scans, patching, log reviews, access reviews, backup tests, training.
  • Technical captures that name the system and date: MFA, encryption, baselines, audit logging, boundary controls.
  • External provider section: flow-down language, provider standing, and who owns each shared objective.
  • A self-assessment trail: gaps found, how each was closed, and the SPRS score that follows from the file as it stands.

Run a self-assessment that is allowed to find problems

The last step of CMMC assessment preparation is a scored self-assessment against the same objectives the C3PAO will use — run early enough that a not-met objective is still a work item rather than a result. Score conservatively. An objective supported by a policy alone, with no record behind it, is not met yet, and marking it met in the file only moves the disappointment to a more expensive room.

Then close the loop in order: fix scope and SSP mismatches first, because they affect every other practice; close evidence gaps where the control exists but the record does not; and only then schedule around the remaining implementation work, remembering the 180-day POA&M window and its eligibility limits if a conditional status is the realistic outcome. Update the SPRS score from the scored file, not from optimism, and have the senior official who will affirm understand exactly what the file shows.

Defense contractor cybersecurity that survives assessment is rarely dramatic. It is a declared scope, controls that leave records as they run, and an evidence file indexed so an assessor can move from objective to proof without a guide. Build that file while there is still time to fix what it reveals, and the assessment becomes what it should be: a verification of work already done, not a test of how fast a team can reconstruct a year in a month.

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions.

Not sure your evidence file would let an assessor find the proof, objective by objective?

NeoSystems ISG is a managed IT, hosting, Microsoft cybersecurity, and CMMC compliance provider built for government contractors: managed hosting, Microsoft 365 GCC and GCC High, cybersecurity, and CMMC compliance support.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

NeoSystems ISG · UEI K5S3DCMK6SJ4 · CAGE 332H1

← Back to Blog

FedRAMP & Federal Cloud · GCC High

GCC High: When ITAR and Export-Controlled Work Make It the Only Tenant That Fits

GCC High is not an upgrade to buy on speculation. When ITAR data, export-controlled technical data, or a contract clause puts U.S.-person and boundary requirements on your email and files, it is the tenant the work actually requires — and when it does not, GCC may be enough.

Secure operations wall with a gold world map and export routes stopping at a glowing boundary, a controlled technical blueprint and a shield emblem beside an aerospace facility at dusk, in navy and gold

GCC High is not an upgrade tier to buy on speculation. It is the Microsoft cloud built for a specific kind of work: contracts where Controlled Unclassified Information (CUI) includes ITAR-controlled technical data or other export-controlled information, and where who can see the data — and where it can sit — is regulated as strictly as how it is encrypted. When that is your work, GCC High is usually the only Microsoft tenant that fits. When it is not, Microsoft 365 GCC or a well-run commercial setup may serve you better, and the money is better spent elsewhere.

The mistake runs in both directions. Contractors buy GCC High because it sounds like the safest answer, then pay the separate-tenant cost and migration effort for a requirement they never had. Others run export-controlled drawings through an ordinary tenant because email is email, and discover the problem in a prime’s audit or, worse, in an export investigation. The decision should start with the data and the clauses, not the product name.

The trigger is the data and the clause, not the logo

Start with what you actually hold. ITAR — the International Traffic in Arms Regulations — controls defense articles and their technical data, and as a rule that technical data may be shared only with U.S. persons unless a license or exemption covers the disclosure. Export-controlled information under the EAR raises the same kind of question with different lists and thresholds. The practical consequence is the same: your email, file shares, and collaboration tools become part of an export-control boundary, not just an IT system.

Then read the contract. DFARS 252.204-7012 requires safeguarding covered defense information and requires that a cloud service provider handling it meet security requirements equivalent to the FedRAMP Moderate baseline — the floor beneath any of these tenants, and the reason a FedRAMP authorized cloud matters in the first place. On top of that floor, primes and contracting officers regularly specify the environment in writing: GCC High named in the subcontract, in the DD Form 254, or in the customer’s security requirements. When a customer names the tenant, the analysis is over. When it does not, the data itself decides: ITAR technical data in the tenant points to GCC High, because that is the environment built to keep access inside the boundary export law draws.

One test cuts through most debates. If a foreign person — a support engineer, an administrator, an employee without the right status — could open the mailbox or the file and see the technical data, is that an export? If the honest answer is yes, the tenant has to be built so that cannot happen by accident or by default.

GCC High answers the people-and-place questions: who can touch the data, and where it lives. It does not answer the program questions — that part is still yours.

What GCC High actually changes

GCC High is a separate Microsoft cloud, not a setting inside the commercial service. Customer data is stored in U.S. data centers, and the environment is operated for U.S. government and defense customers: access to customer data is limited to screened personnel, and support is delivered by U.S. persons — the property that matters most when the data is export-controlled, because routine vendor support in an ordinary tenant is not screened to that standard. The environment is built to the FedRAMP High baseline and to the Department of Defense’s cloud security requirements for the sensitive unclassified workloads it hosts, which is why it satisfies the DFARS 7012 compliance floor with room to spare.

Two operational consequences follow, and both should be planned rather than discovered. First, GCC High is a separate tenant: licenses are bought for that cloud, mailboxes and files are migrated, and there is no toggle that converts a commercial or GCC tenant in place. Second, feature parity is close but not identical — some applications and integrations arrive later in GCC High, and every connected tool has to be checked against the boundary before it is plugged in, because a commercial add-on with access to GCC High data can quietly re-open the export question you just closed.

What GCC High does not settle

A correct tenant is not an export-control program. ITAR obligations — registration where it applies, license determinations before anything is shared, a technology control plan that says who may access what, and training for the people inside the boundary — belong to the company, and no cloud purchase discharges them. GCC High narrows who can reach the data from the platform side. Your access reviews, your hiring and onboarding checks, and your sharing settings decide who does.

The same holds for the rest of DFARS 7012 compliance. Identity rules, conditional access, external sharing, audit logging, and guest access are still tenant configuration you own, exactly as they are in GCC. Incident response still runs on your 72-hour clock. Subcontractor flow-down still runs through you: a supplier who receives your ITAR data needs its own compliant home for it, and putting that supplier’s name in your tenant without checking its status exports your problem instead of solving it. And the System Security Plan still has to describe this tenant, this boundary, and this data — a GCC High logo in the SSP is not a scope statement.

The GCC High decision checklist

  • Inventory the data: does any tenant content include ITAR technical data or other export-controlled information?
  • Read the clauses and the DD Form 254: does a contract, subcontract, or prime requirement name GCC High or set U.S.-person access?
  • Apply the access test: could a non-U.S. person — vendor support, admin, or staff — reach the data in your current tenant?
  • Check every connected app and add-on against the boundary before migration, not after.
  • Plan it as a migration: separate tenant, separate licensing, staged mailbox and file moves, and a cutover that keeps delivery running.
  • Pair the tenant with the program: technology control plan, training, access reviews, and the SSP updated to describe the new boundary.

Decide before the migration, not during it

The contractors who get this right treat tenant selection as a scoping decision with evidence behind it: a data inventory that names the export-controlled content, the contract language that applies to it, and a written conclusion about which tenant the combination requires. That record is useful three times over — it justifies the spend to leadership, it answers the prime’s questionnaire without improvisation, and it gives the assessor a boundary that matches the systems diagram.

If the inventory shows no export-controlled data and no contract names the environment, GCC High is likely more tenant than you need, and the disciplined move is to run GCC well and spend the difference on the controls an assessor will actually test. If the inventory shows ITAR data, or the next subcontract may bring it, decide now, while the migration can be planned and priced — not after the data has already landed somewhere it should never have been.

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions.

Not sure whether your contracts and data actually require GCC High — or whether your current tenant is already out of bounds?

NeoSystems ISG is a managed IT, hosting, Microsoft cybersecurity, and CMMC compliance provider built for government contractors: managed hosting, Microsoft 365 GCC and GCC High, cybersecurity, and CMMC compliance support.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

NeoSystems ISG · UEI K5S3DCMK6SJ4 · CAGE 332H1

← Back to Blog

GovCon IT, Cybersecurity & Industry Developments · CISA KEV

GovCon IT Services on a Three-Day Clock: What November's KEV Surge Requires From Contractors

CISA added ten exploited flaws to the KEV Catalog on November 9–10, 2026. The federal deadline was three days for the first batch. What that pace requires from contractors — inventory, triage before patching, and a record that holds up.

Secure operations center at dusk in front of a federal office building, a wall display with gold three-day patch timeline markers and a shield emblem, in navy and gold

GovCon IT services used to be judged on a monthly patch rhythm: scan, prioritize, patch on the next window, document. That rhythm no longer matches the federal clock. On November 9, 2026, CISA added four vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog based on evidence of active exploitation, with a November 12 remediation deadline for federal civilian agencies. On November 10, it added six more. Ten confirmed-exploited flaws in two days — in file transfer, telephony, remote access, email security, and the browser and mail client on nearly every desk — is not a routine patch week. It is a test of whether a contractor’s vulnerability process can move in days, with evidence, without waiting for the next maintenance window.

The deadline itself binds only Federal Civilian Executive Branch agencies under Binding Operational Directive (BOD) 26-04. No contractor should misread that as distance. Primes, agencies, and assessors increasingly ask the same question BOD 26-04 asks: when a flaw is known to be exploited, how fast did you find it in your environment, triage whether you were already compromised, and close it — and can you show the record?

What landed on November 9 and 10

The November 9 batch covered four very different parts of a contractor’s estate. CVE-2026-102895 is an improper authentication flaw in GPUStack, the platform some teams use to run AI models across GPU machines. CVE-2026-116779 is a code injection flaw in SignalWire FreeSWITCH, the open-source telephony platform. CVE-2026-123158 is a flaw in OpenBSD OpenSSH that, in a specific and common Linux configuration, becomes an authentication bypass for remote access. CVE-2026-123218 is an incorrect authorization flaw in IBM Aspera Faspex 5, an enterprise file-transfer product — the kind of tool that, in a GovCon environment, may move exactly the files a contract cares most about.

The November 10 batch widened the blast radius to the everyday edge: CVE-2026-20320 in Cisco BroadWorks, CVE-2026-111560 and CVE-2026-116606 in Barracuda Networks products including its Email Security Gateway, CVE-2026-111793 in Openwave Messaging’s Webtop Media Transcoder, CVE-2026-124194 in Microsoft Office Outlook, and CVE-2026-125350, a use-after-free flaw in Google Chromium. Two of the six sit in email and communications platforms. Two more — Outlook and Chromium — live on effectively every endpoint. Government contractor cybersecurity fails or holds in precisely those places: identity, email, remote access, and file movement.

A KEV listing is not a warning that a flaw might be used. It is CISA’s statement that it is being used. The work that follows is triage first, patching second, in that order.

What BOD 26-04 actually changed

BOD 26-04, “Prioritizing Security Updates Based on Risk,” does not tell agencies to patch everything instantly. It tells them to prioritize — fast — the KEV flaws on publicly exposed assets that grant total control of the asset after exploitation, and to defer lower-risk items behind them. It also establishes a baseline expectation agencies often miss in summaries: check whether threat actors compromised the system before the patch was applied. Listing is treated as a signal that compromise may already have happened, not only as a warning about future risk.

That triage-first logic is the part contractors should adopt even though the directive does not bind them directly. Patching a compromised file-transfer server without checking what it transferred, or patching an edge gateway without reviewing its logs for the exploitation window, closes the hole and destroys the answer to the more important question. For a contractor holding Controlled Unclassified Information (CUI), that question connects straight to DFARS 252.204-7012: if the exploitation touched covered defense information, the 72-hour incident reporting clock and the forensic record that supports it start from discovery, not from the patch ticket’s close date.

Why this is a compliance problem, not only a patching problem

NIST SP 800-171 has required this discipline all along, in plainer language. Risk Assessment (RA.L2-3.11.2 and RA.L2-3.11.3) requires periodic scanning and prompt remediation of identified flaws. System and Information Integrity (SI.L2-3.14.1) requires identifying, reporting, and correcting flaws in a timely manner. Audit and Accountability requires the logs that make triage possible. A three-day KEV deadline does not create a new control family — it compresses the time in which those existing controls have to produce a record an assessor, a prime, or an incident investigator can follow.

That is where federal contractor compliance is won or lost in a week like this one. The contractors who struggle are rarely missing a scanner. They are missing an accurate inventory — they cannot say quickly whether FreeSWITCH, Aspera Faspex, or a musl-based OpenSSH image exists anywhere in their estate, including in a lab, a container image, or a subcontractor’s corner of the network. They are missing a pre-agreed triage order, so every critical flaw becomes an argument about the maintenance window. And they are missing the habit of writing the decision down: found or not found, exposed or internal, compromised or no evidence of compromise, patched or mitigated or removed — with dates.

The three-day KEV playbook for contractors

  • Match the KEV entry to your inventory the same day: product, version, and where it runs — including containers, labs, and edge appliances, not only the production list.
  • Triage before you patch where exploitation is plausible: preserve logs and check for compromise on the affected asset first, per the BOD 26-04 expectation.
  • Patch, mitigate, or take the asset offline in that order of preference — and if no fix can be applied, document the compensating control and the owner who accepted the risk.
  • If CUI or covered defense information may be involved, start the DFARS 7012 assessment immediately; do not wait for patch confirmation to decide whether the 72-hour clock applies.
  • Record the whole sequence with dates — discovery, triage result, remediation, verification scan — in the same file your SSP and POA&M point to.
  • Flow the same expectation down: ask subcontractors and your own IT providers for their KEV response on the affected products, in writing.

What to fix in the process before the next batch

CISA will add more entries next week; the catalog’s pace in 2026 guarantees it. The durable fix is not heroic effort on a three-day deadline. It is a standing KEV lane in your vulnerability process: KEV additions reviewed daily, a named owner who can authorize an emergency change without a committee, pre-approved maintenance language in client and subcontractor agreements, and an inventory accurate enough that “do we run this?” is a query, not a project.

Test that lane honestly. Pick the November 10 Outlook flaw and ask how long it would take your team to say which endpoints run the affected version, push the fix, and prove completion. Pick the Aspera Faspex flaw and ask who would run the pre-patch compromise check, and where those logs live. If either answer starts with “we would need to find out,” that finding — not any single CVE — is the remediation item, and it belongs on the POA&M until the lane exists.

GovCon IT services are increasingly measured this way: not by the tools a provider lists, but by the hours between a federal signal and a documented result in your environment. November’s ten listings gave every contractor a free rehearsal. Use the record of how your team actually responded — good or bad — while it is still fresh, and close the gaps it exposed before a listing names a product at the center of your CUI boundary.

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions.

Not sure your team could answer “do we run this, were we hit, and is it closed” within three days of the next KEV batch?

NeoSystems ISG is a managed IT, hosting, Microsoft cybersecurity, and CMMC compliance provider built for government contractors: managed hosting, Microsoft 365 GCC and GCC High, cybersecurity, and CMMC compliance support.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

NeoSystems ISG · UEI K5S3DCMK6SJ4 · CAGE 332H1

← Back to Blog

CMMC Compliance · Affirmation & SPRS

CMMC Level 2 Certification and the Annual Affirmation: What Your Senior Official Is Actually Signing

Certification is not the finish line. Under 32 CFR Part 170, a senior official must affirm in SPRS every year that your company still implements the CMMC requirements — here is the evidence routine that makes signing defensible.

Senior executive signing a formal compliance document at a desk in front of a federal office building at dusk, gold shield emblem, in navy and gold

CMMC Level 2 certification is often treated as the finish line: pass the assessment, receive the certification, file the result, and move on. The affirmation requirement in 32 CFR Part 170 says otherwise. After certification — and then every year while the certification is in effect — a senior official from your organization must affirm in SPRS that your company continues to implement the CMMC requirements. That signature is not a clerical step. It is a company-level statement, made by someone with authority to speak for the business, that the CMMC compliance posture described in your System Security Plan (SSP) is still true.

That matters because environments drift. People leave, tools are replaced, a cloud service is added for convenience, an exception granted for a week becomes permanent. None of that automatically invalidates a certification on the day it happens — but all of it can make the next annual affirmation hard to sign honestly if nobody has been checking. Contractors who build a light, regular affirmation routine sign with confidence. Contractors who treat the affirmation as a calendar reminder discover, once a year, that they are being asked to attest to a year nobody actually verified.

What the affirmation covers — and what it does not forgive

The affirmation follows the assessment or self-assessment result entered in SPRS. For Level 2 certification, a senior official affirms continuing compliance after the C3PAO assessment and annually thereafter. The affirmation does not re-run the assessment, and it does not ask the official to personally inspect firewall rules. It asks the organization to stand behind its status — which means the organization, not just the signer, needs a basis for that statement.

Two consequences follow. First, a material change that breaks a practice — moving CUI into a system outside the assessed scope, dropping multifactor authentication for a group of users, letting a POA&M item age past its committed date — is not cured by having passed last year. If the practice is no longer met, the honest course is to fix it, update the SSP and the SPRS score where the rules require it, and only then affirm. Second, the affirmation creates a record. Primes reviewing flow-down, contracting officers checking status, and assessors returning for the next cycle will all read that record as your company’s own statement about itself. Signing carelessly is therefore not only a compliance risk; it is a credibility risk with the customers who sent the requirement down to you in the first place.

The affirmation is short. The work that makes it true is the other 364 days: change control, scope discipline, and records that show the controls kept running after the assessors left.

Build the affirmation file before anyone is asked to sign

The practical answer is an affirmation file — a small, standing packet that is updated through the year and handed to the senior official before the SPRS affirmation comes due. It should let a busy executive verify, in one sitting, that the certification still describes reality.

Start with scope. Confirm the CUI boundary in the SSP still matches the network diagrams, the asset inventory, and the cloud services actually in use. List every material change since the assessment: new systems, retired systems, new external service providers, office or enclave changes. For each change, note how the affected NIST SP 800-171 practices were reviewed. Scope drift is the most common reason an affirmation becomes difficult, and it is also the easiest to catch early.

Next, show operating evidence across the year, not a single recent week: vulnerability scan summaries and remediation records, patch reporting, log-review records, access reviews with removals shown, incident-response exercises or real incidents and how they were handled, backup test results, and security awareness training completion. This is the same evidence discipline good CMMC assessment preparation builds — reused here to prove continuity rather than initial readiness.

Then close the open items. List every POA&M item, its current status, and whether it is still inside its committed window. List any practice that became not met during the year, how it was corrected, and whether the SSP and SPRS entries were updated to match. An affirmation file that names its own problems and shows them closed is far stronger than one that claims nothing ever changed.

The annual affirmation packet, in one page

  • Scope statement: current CUI boundary, asset inventory date, and every material change since assessment — with the practice review for each.
  • Operating records across the year: scans, patching, log reviews, access reviews, backup tests, training, and incident-response activity.
  • POA&M status: every open item, its owner, and whether it remains inside its committed completion window.
  • Exceptions and lapses: any practice that became not met, how it was fixed, and what was updated in the SSP or SPRS as a result.
  • Provider check: external service providers still in scope, their current standing, and any change in shared responsibility.
  • A one-paragraph recommendation to the senior official: affirm as-is, or hold the affirmation until a named item is closed.

Give the senior official a real review, not a signature request

How the affirmation is presented inside the company matters. A signature request that arrives as a link and a deadline invites a reflexive click. A short review meeting — the packet above, thirty minutes, the people who operate the controls in the room — turns the affirmation into what the regulation intends: an accountable official making an informed statement.

In that review, three questions do most of the work. Does the assessed scope still contain all the places CUI actually lives, and nothing has quietly moved outside it? Are there any practices we know are not met today, even temporarily? And if a prime or an assessor asked us tomorrow to show the basis for this affirmation, would this packet be enough? If any answer is no, the correct move is to pause, fix the item, and document the fix — not to sign and hope the next assessment is far away.

This is also where flow-down discipline pays off. Subcontractors who hold your CUI make their own affirmations, and your affirmation implicitly leans on theirs. Ask subs for their current status and affirmation dates as part of the same annual cycle, and keep their answers in the packet. A prime will ask you the same question; having the file ready is the difference between a same-day answer and a scramble.

Treat the affirmation date as a deadline you work backwards from

Put the affirmation on the compliance calendar with lead time: packet assembled sixty days out, review meeting thirty days out, corrections closed before the due date, affirmation entered in SPRS on time. That rhythm costs a few hours a quarter to maintain. The alternative — reconstructing a year of scope changes and control records under deadline pressure, with a senior official waiting to sign — costs more, and produces a weaker statement either way.

CMMC Level 2 certification proves your environment met the requirements when it was assessed. The annual affirmation is how your company says, in its own name, that it still does. Build the file that makes that statement easy to verify, and the signature becomes the smallest part of the process — which is exactly what it should be.

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions.

Not sure your senior official could sign the next affirmation from evidence rather than memory?

NeoSystems ISG is a managed IT, hosting, Microsoft cybersecurity, and CMMC compliance provider built for government contractors: managed hosting, Microsoft 365 GCC and GCC High, cybersecurity, and CMMC compliance support.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

NeoSystems ISG · UEI K5S3DCMK6SJ4 · CAGE 332H1

← Back to Blog

GovCon IT & Cybersecurity · Industry Developments

Federal Contractor Compliance After November 10: The Deadline Passed, the Duties Did Not

CMMC Phase 2 remains suspended and November 10 came and went — but DFARS 7012, SPRS self-assessments, and rapid KEV triage are what primes are enforcing now. Here is the compliance check that matters this week.

Compliance operations desk with a November calendar page, shield emblem and contract documents in front of a federal office building at dusk, gold network lines, in navy and gold

Federal contractor compliance had a date circled for a year: November 10, 2026, when CMMC Phase 2 was scheduled to begin. That date has now passed, and Phase 2 did not begin. The Department suspended the Phase 2 transition on July 13, 2026, and Class Deviation 2026-O0025, Revision 3, later wrote that suspension into contracting language. No replacement date has been published. For a contractor deciding where to spend the next compliance dollar, that sounds like a pause. It is not. The duties underneath CMMC — safeguarding, self-assessment, incident reporting, and fast response to exploited flaws — never paused, and they are what primes, contracting officers, and assessors are enforcing today.

That distinction is the whole story of federal contractor compliance this month. The third-party certification requirement that Phase 2 would have added as a condition of award is suspended. Everything a contractor was supposed to be doing to get ready for it is still required, still checked, and still capable of costing a bid or a contract if the record is weak.

What actually changed when November 10 passed

Under the suspension, requiring activities may still write CMMC Level 1 (Self) or Level 2 (Self) into solicitations. What they may not do, under the current deviation, is impose the suspended Level 2 (C3PAO) certification requirement as the Phase 2 transition would have required. Solicitations that still carry that language are being amended, and contracts that hold suspended requirements are to be modified before the next option period or at the next scheduled administrative modification.

Read that carefully and two practical points emerge. First, the solicitation in front of you — not a headline about the program — still decides what you must hold at award. Check DFARS 252.204-7025 for the level named, and check that your status for that level is current in SPRS for the systems that will handle Federal Contract Information or Controlled Unclassified Information (CUI). Second, a suspended certification deadline is not a suspended safeguarding duty. DFARS 252.204-7012 still requires adequate security under NIST SP 800-171, and DFARS 252.204-7019 and 7020 still require a current NIST SP 800-171 assessment in SPRS.

November 10 removed a certification deadline. It did not remove a single safeguarding, scoring, or reporting duty that was already in your contract.

Self-assessment is now the enforcement surface

With third-party certification paused, government contractor cybersecurity is being judged, for most contractors, on the honesty and currency of the self-assessment. That raises the stakes on work some teams treated as paperwork. A SPRS score is a company statement. If the score claims a practice is implemented and the environment does not match — multifactor authentication scoped more narrowly than the plan says, a cloud service holding CUI outside the boundary in the System Security Plan (SSP), a POA&M item long past its committed date — the problem is no longer only a control gap. It is an accuracy problem, and primes know to look for it when they flow requirements down.

The contractors handling this well run a simple discipline. The SSP, the asset inventory, and the SPRS entry describe the same boundary. Every material change — a new tool, a new provider, a moved enclave — triggers a review of the affected NIST SP 800-171 practices before the change is treated as complete. POA&M items have owners and dates that someone actually tracks. None of that requires a C3PAO on site. All of it is what a C3PAO, a prime, or a government-led assessment would test first if one arrived tomorrow.

The other clock did not pause either: exploited flaws

While the CMMC calendar paused, the exploitation calendar accelerated. On November 13, 2026, CISA added a Check Point Gaia flaw, CVE-2026-123039, to its Known Exploited Vulnerabilities (KEV) Catalog with a November 16 remediation deadline for federal civilian agencies. That followed the November 9 batch of four exploited flaws that carried a November 12 deadline. Binding Operational Directive 26-04 binds federal civilian agencies directly; it reaches contractors when their contract directs it, and it reaches the systems contractors run on an agency’s behalf because those systems are in scope.

Even where no contract clause imports the KEV deadline word for word, the pattern matters for federal contractor compliance. NIST SP 800-171 already requires timely flaw remediation, vulnerability scanning, and the audit records that make triage possible. A three-day federal deadline for a flaw in a gateway or remote-access product is a public measure of what “timely” now means when exploitation is confirmed. A contractor that learns about a KEV listing from its prime, a week later, has a process finding — regardless of whether that specific CVE was ever in its estate.

DFARS incident reporting connects here directly. If triage of a KEV-listed product finds evidence that covered defense information may have been affected, the DFARS 252.204-7012 reporting duty — rapid reporting within 72 hours of discovery, with the forensic record to support it — starts from discovery, not from when the patch ticket closes. Patching first and asking questions later can close a hole and lose the evidence the report requires.

The post-November 10 compliance check, in one pass

  • Read the live solicitation: confirm which CMMC level DFARS 252.204-7025 names, and that your SPRS status for that level is current.
  • Reconcile three documents: SSP boundary, asset inventory, and SPRS entry must describe the same systems — including cloud services and providers that touch CUI.
  • Audit your POA&M for honesty: every item owned, dated, and inside its committed window, or updated before a prime finds it stale.
  • Run the KEV lane daily: match new CISA KEV additions to your inventory the same day, triage for compromise before patching where exploitation is plausible, and record the sequence with dates.
  • Rehearse the 72-hour DFARS incident reporting path: who decides, who reports, and where the logs that support the report live.
  • Ask subcontractors for current status in writing — their self-assessment is part of the record your own compliance leans on.

What primes are asking for now

In the absence of a certification to point to, primes are asking for the evidence behind the self-assessment: a current SPRS score and the date it was posted, the SSP boundary statement, POA&M status, and increasingly, how fast the contractor responded to recent KEV listings in products it actually runs. Those are reasonable questions, and they are hard to answer retroactively. A contractor that can produce them in a day signals the same thing a certification was meant to signal — that the controls are real and maintained — using the only currency available while Phase 2 is suspended.

That is also the right way to use the pause itself. Contractors who wanted a C3PAO assessment for their own risk posture, or because a prime’s expectations run ahead of the suspended requirement, can still pursue one voluntarily. Contractors who are not ready should treat the suspension as borrowed time with a specific purpose: close the scope, evidence, and response-speed gaps that a self-assessment now exposes, while the cost of fixing them is still a project rather than a lost award.

Federal contractor compliance after November 10 is therefore simpler than the headlines suggest, and stricter than a pause implies. Hold the level your solicitation names, keep the SPRS record honest and current, protect CUI under NIST SP 800-171 as DFARS 7012 has always required, answer exploited flaws in days with a record, and keep the 72-hour reporting path ready. Do those five things well, and the eventual return of Phase 2 — on whatever date the Department publishes — becomes a scheduling question, not a scramble.

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions.

Not sure your self-assessment, SPRS record, and KEV response would hold up if a prime asked for the evidence this week?

NeoSystems ISG is a managed IT, hosting, Microsoft cybersecurity, and CMMC compliance provider built for government contractors: managed hosting, Microsoft 365 GCC and GCC High, cybersecurity, and CMMC compliance support.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

NeoSystems ISG · UEI K5S3DCMK6SJ4 · CAGE 332H1

← Back to Blog

FedRAMP & Federal Cloud · DFARS 7021

DFARS 7021 Compliance: What the Clause Requires From Your Cloud Providers Before Award

DFARS 252.204-7021 ties your CMMC status to every cloud service and external provider that touches CUI. Here is how to check authorization, equivalency, and status — with evidence — before award, not after a finding.

Secure cloud operations wall in front of a federal office building at dusk, gold network lines connecting a contractor office to authorized cloud data centers, a shield emblem and contract document, in navy and gold

DFARS 7021 compliance is where a contractor’s CMMC status stops being only about its own network. DFARS 252.204-7021 is the clause that requires a contractor to maintain the CMMC level the contract calls for, and it reaches every system that stores, processes, or transmits Controlled Unclassified Information (CUI) — including the cloud services and external providers that hold that CUI on the contractor’s behalf. Choose a provider that cannot meet the standard, and the gap is not the provider’s problem in an assessment. It is yours.

That reach is routinely underestimated. A team scopes its own enclave carefully, writes its System Security Plan around that boundary, and then discovers that email, file storage, a help-desk tool, or a managed hosting platform sitting outside the plan is also handling CUI — under rules the team never checked. DFARS 7021 compliance requires that check to happen before the provider is used, not after an assessor or a prime asks for the paperwork.

What 7021 actually adds to 7012

DFARS 252.204-7012 is the safeguarding and incident-reporting clause: protect covered defense information, use cloud services that meet security requirements equivalent to the FedRAMP Moderate baseline, and report incidents rapidly. DFARS 252.204-7021 builds the CMMC requirement on top of it. Where a contract includes 7021 and specifies a CMMC level, the contractor must have and maintain that level for all systems that handle the relevant Federal Contract Information or CUI, and must flow the requirement down to subcontractors whose work involves that information.

Two practical consequences follow for cloud decisions. First, status has to be current at award and maintained through performance — a provider or subcontractor that was compliant when a proposal was written is not enough if its status lapses mid-contract. Second, the clause makes your providers part of your compliance surface. Their authorization, their assessment status, and the split of responsibilities between them and you all become evidence in your own file.

Cloud service providers: authorization or equivalency, documented

For cloud services that store, process, or transmit CUI, the standard is specific. Under the CMMC program in 32 CFR Part 170, a cloud service provider used for CUI must be FedRAMP authorized at the Moderate baseline or be documented as FedRAMP Moderate equivalent. A FedRAMP authorized cloud listing is the cleanest evidence: the service, in the exact form you use it, appears in the FedRAMP Marketplace with an authorization you can cite in your SSP.

Equivalency is narrower than marketing often makes it sound. It is not a provider’s statement that it follows FedRAMP controls, uses FedRAMP-aligned hosting underneath, or will complete authorization later. Equivalency means the provider meets the FedRAMP Moderate requirements and can produce the evidence an assessor expects for that claim — the body of evidence behind the authorization decision, not a logo or a one-page letter. If a provider says “equivalent,” ask what evidence supports the word, who reviewed it, and whether it covers the specific service and boundary you would use. If those answers are vague, treat the service as unproven for CUI until they are not.

This is why tenant choice matters in practice. Microsoft 365 GCC is built on FedRAMP-authorized services for government workloads, and GCC High is built for the more demanding cases, including ITAR and stricter contract requirements. In either tenant, the authorization covers the platform as assessed — not every add-on, connector, or third-party tool a team later plugs into it. Each connected service that touches CUI needs its own check.

7021 does not ask whether a provider sounds compliant. It asks whether you can show, service by service, that the providers holding your CUI meet the standard — and that you checked before award, not after a finding.

Other external providers are not a loophole

Not every external service provider is a cloud service provider, and the distinction matters — but it does not create a loophole. A managed service provider, a security operations provider, or another external provider that works inside your CUI boundary, or that can access CUI through the support it provides, sits inside your assessment scope in a different way. Its personnel, its tools, and its access paths affect how your own practices are implemented, and an assessor will examine that relationship.

For those providers, the work is scoping and documentation: name the provider in the SSP and the asset inventory, describe exactly what it can access and what it cannot, record how its work is controlled and reviewed, and keep the customer responsibility matrix that separates its duties from yours. A provider that refuses to be described that plainly, or that cannot explain how it protects the access it holds, is telling you something an assessment would confirm later at higher cost.

Flow it down, and check status, not promises

Flow-down is the other half of DFARS 7021 compliance. When you subcontract work that involves CUI at the level your contract requires, the subcontract must carry the requirement, and the subcontractor must hold the appropriate CMMC status before award of that subcontract. The same provider check applies one tier down: a subcontractor’s cloud choices become part of the chain a prime will eventually ask you to explain.

Make the check a record, not a conversation. For each provider and subcontractor in the CUI chain, keep the service name and boundary, the authorization or equivalency evidence you reviewed, its CMMC status where it applies and the date you verified it, the responsibility matrix, and the contract language that flows the requirement down. Re-verify on a schedule and at renewal — status changes, authorizations are updated, and services are added quietly by well-meaning teams throughout the year.

The 7021 provider check, before award

  • List every cloud service and external provider that stores, processes, transmits, or can access CUI — including add-ons and support tools, not only the main tenant.
  • For each cloud service, cite the FedRAMP authorization for the exact service, or collect the full equivalency evidence behind the claim.
  • Confirm CMMC status for subcontractors at the required level before award, and record the date and source of the check.
  • Write the responsibility split for each provider into the SSP: what it implements, what you implement, and what is shared.
  • Flow 7021 down in writing, and re-verify provider and subcontractor status at renewal and on a regular schedule.
  • Remove or replace any provider that cannot produce evidence — before CUI moves into it, not after.

Decide with evidence while you still have options

The cheapest time to solve a provider problem is before data moves. Replacing an email tenant, a file platform, or a hosting provider after CUI has lived there for a year means migration, re-scoping, and an SSP rewrite under deadline. Checking authorization, equivalency, and status during selection costs a few direct questions and a file that records the answers.

Contractors who handle DFARS 7021 compliance well treat provider selection as a compliance decision with the same weight as their own controls: no evidence, no CUI. That discipline protects the assessment, it protects the award, and it gives a prime a clean answer when the prime asks the question 7021 was written to make unavoidable — who else holds this information, and how do you know they meet the standard?

NeoSystems ISG Team

Managed IT, hosting, Microsoft cybersecurity, and CMMC compliance for government contractors — a 20-year GovCon practice, rebuilt under new ownership and backed operationally by FIT Solutions.

Not sure whether every cloud service and provider in your CUI chain would pass a DFARS 7021 check today?

NeoSystems ISG is a managed IT, hosting, Microsoft cybersecurity, and CMMC compliance provider built for government contractors: managed hosting, Microsoft 365 GCC and GCC High, cybersecurity, and CMMC compliance support.

Or reach us directly: contact@neosystemsisg.com · (866) 556-7140

NeoSystems ISG · UEI K5S3DCMK6SJ4 · CAGE 332H1

Contact

Contact Us Today

Tell us about your contract requirements, your timeline, and where your compliance stands today. A person — not a bot — will get back to you.

Talk to us directly

Prefer email or phone? Use either — both are answered by the team.

Email

contact@neosystemsisg.com

Phone

(866) 556-7140

Common reasons contractors call:
• A CMMC Level 2 flow-down just landed in a contract
• You need GCC High for CUI or ITAR work
• Your SPRS score isn’t where a prime needs it
• Your current provider went dark — we understand that one personally

NeoSystems ISG is owned by NSISG Holding LLC and backed operationally by FIT Solutions.

Request a consultation

Complete the form and we’ll open a pre-addressed email to our team with your details — nothing is sent until you confirm it in your mail app.

Thank you — your email draft is ready. If it didn’t open, write to contact@neosystemsisg.com or call (866) 556-7140.

Submitting opens your email client addressed to contact@neosystemsisg.com. Prefer to skip the form? Email or call us directly anytime.

Primes & Teaming Partners

Subcontracting or building a team? NeoSystems ISG supports primes with CMMC-ready hosting, GCC and GCC High environments, and managed cybersecurity your program can flow down with confidence. Start the conversation at contact@neosystemsisg.com or (866) 556-7140.